- الرئيسية >
- مفسرون >
- أدوات SIEM
أفضل حلول SIEM: أفضل 11 نظام SIEM وكيفية الاختيار 2026
- 11 minutes to read
فهرس المحتويات
افهم كيف يمكن أن تساعد أنظمة SIEM في حماية عملك وتعرف على بعض من أفضل حلول SIEM. SIEM توفر الحلول عرضًا موحدًا للأحداث الأمنية، مما يجعلها مكونًا أساسيًا من SIEM توفر الحلول عرضًا موحدًا للأحداث الأمنية، مما يجعلها مكونًا أساسيًا من الأمن السيبراني. هذه المقالة ذات صلة لأي شخص لا يفهم تمامًا كيف تعمل حلول أمان SIEM ولماذا هي مكون حاسم في الأمن السيبراني. سنناقش المزايا الرئيسية لاستخدام أنظمة SIEM بالإضافة إلى بعض من أفضل بائعي SIEM ولماذا تعتبر منتجاتهم فريدة.
Editor’s note: Updated the article to cover recent market trends, updated information for SIEM solutions to reflect features and capabilities in 2026.
هذا المحتوى هو جزء من سلسلة حول أدوات SIEM.
ما هو SIEM وكيف يعمل؟
إدارة معلومات وأحداث الأمان (SIEM) هي نظام للكشف عن التهديدات يقوم بتركيز التنبيهات الأمنية القادمة من مصادر متعددة للمراجعة والإجراء، ويقوم بإنشاء تقارير الامتثال.
تستخدم حلول SIEM تجميع البيانات وتوحيدها لتوفير رؤية متكاملة لجميع الأحداث الأمنية في منصة واحدة. يمكن للمستخدمين اكتشاف التهديدات في الوقت الحقيقي ولم يعد المحللون الأمنيون بحاجة إلى إضاعة الوقت في البحث عن جميع الإشعارات التي تولدها مكونات البحث عن التهديدات والمراقبة المختلفة.
بالإضافة إلى SIEM، يمكن للموظفين الأمنيين تعريف الأنشطة العادية وغير العادية باستخدام القواعد. تقدم الحلول الأكثر تقدمًا، المعروفة باسم SIEMs من الجيل التالي، التعلم الآلي والذكاء الاصطناعي لتحديث تحليلات سلوك المستخدم والكيان (UEBA) نماذج سلوكية باستمرار لتقليل الإيجابيات الكاذبة. في SIEMs من الجيل التالي، يتم تحليل البيانات التي تجمعها نظام SIEM بالنسبة للقواعد المحددة وأنماط السلوك المعروفة. في أي وقت يتم فيه اكتشاف نشاط غير عادي، يتم إنشاء حدث ملحوظ للمراجعة.
توفر حلول SIEM حماية مخصصة للأمن السيبراني بناءً على قواعد محددة مسبقًا، وتوافقات بين الأحداث الأمنية، والتعلم الآلي. كما أنها تخزن بيانات السجلات على مر الزمن، مما يسهل البحث عن المعلومات التاريخية وإعداد تقارير الامتثال.
Understanding the SIEM Solutions Market
According to recent market research, the global SIEM market is expanding steadily. It is valued at USD 10.67 billion and is projected to reach USD 20.78 billion by 2031, growing at a CAGR of 11.5%. This growth is driven by increasing regulatory pressure, rapid cloud adoption, and the rising scale of security telemetry.
Organizations are modernizing correlation engines and analytics to handle larger data volumes. At the same time, stricter breach disclosure laws in North America, Europe, and Asia-Pacific are forcing faster detection and reporting. These factors are supporting continued investment in SIEM platforms.
Key Market Drivers
One major driver is the sharp increase in log and telemetry data. Large enterprises now ingest more than 10 TB of logs per day from endpoints, cloud services, SaaS platforms, and operational technology. This growth requires scalable storage models such as tiered retention and streaming analytics pipelines.
Regulatory enforcement is another strong factor. Frameworks such as the European NIS2 Directive and the U.S. SEC cybersecurity disclosure rules require timely incident reporting and proper log retention. Financial institutions in Europe must also test SIEM-based response processes regularly under DORA requirements.
Cloud and hybrid adoption are also accelerating SIEM demand. By 2025, 60% of enterprise compute workloads had shifted to public cloud. Cloud-native SIEMs integrate directly with provider APIs, reducing deployment time and enabling centralized visibility across distributed environments.
AI and machine learning are improving alert quality. Vendors are embedding large language models and AI assistants into SIEM workflows to summarize incidents, reduce low-value alerts, and guide response steps. This improves analyst productivity and reduces mean time to respond.
Deployment Trends
On-premises SIEM systems still held 55.27% of the market share in 2025. However, cloud deployments are growing faster, with a projected CAGR of 12.84% through 2031.
Cloud models reduce infrastructure management overhead and support elastic scaling. Hybrid approaches are common in regulated industries, where sensitive logs remain on-premises while analytics run in the cloud.
Legacy platforms accounted for 48.12% of revenue in 2025, but cloud-native architectures are growing steadily. Modern designs separate storage and compute, allowing organizations to store raw logs in low-cost object storage and run queries only when needed.
أفضل 10 حلول لإدارة معلومات وأحداث الأمان (SIEM)
أصبح نظام SIEM مكونًا أساسيًا في الأمن السيبراني. ومع ذلك، ليست جميع حلول SIEM متساوية. عند اتخاذ القرار بشأن أي نظام SIEM يجب اعتماده، من المهم أن نضع في اعتبارنا أن SIEM ليس حلاً معزولًا، بل يجب أن يكون جزءًا من استراتيجية أمان أكبر. بعض من أفضل حلول SIEM مدرجة أدناه.
تم الحصول على المعلومات حول قدرات وحواجز حلول SIEM من Gartner Peer Insights ومصادر أخرى متاحة للجمهور.
1. Exabeam Fusion

كمنصة دمج أمني من الجيل التالي، تُعتبر منصة دمج أمني (Exabeam Fusion) حلاً سحابياً يستخدم نهجاً قائماً على السلوك لكشف التهديدات والتحقيق والاستجابة (TDIR). من خلال تجميع جميع الأحداث ذات الصلة واستبعاد الأحداث غير الشرعية، تعزز منصة دمج أمني إنتاجية المحللين وتكتشف التهديدات التي فاتت أدوات أخرى. هذا يُحسن معدلات الكشف ووقت الاستجابة، ويضمن أن جميع التنبيهات تؤخذ بعين الاعتبار - حتى تلك القادمة من الأنظمة "الصاخبة" التي تولد العديد من التنبيهات.
بالإضافة إلى ذلك، فإن Fusion SIEM متكامل بشكل أصلي مع حل الأتمتة والتنسيق الأمني (SOAR)، الذي يوفر استجابة تلقائية للحوادث. وهذا يمكّن من التعامل مع أي تهديد تقريبًا تلقائيًا (أو شبه تلقائي إذا تم تفضيله) في الوقت الحقيقي. تتيح سير العمل التوجيهية ومحتوى حالات الاستخدام المعبأة مسبقًا (التهديدات الخارجية، والمخترقون المتعاونون، والمخترقون الخبيثون) تحقيق نتائج ناجحة لمركز العمليات الأمنية وأتمتة الاستجابة. كما يوفر Fusion SIEM أيضًا تخزين السجلات المستند إلى السحابة، والبحث السريع والموجه، وتقارير الامتثال الشاملة المتوقعة من أي SIEM حديث.

2. Securonix

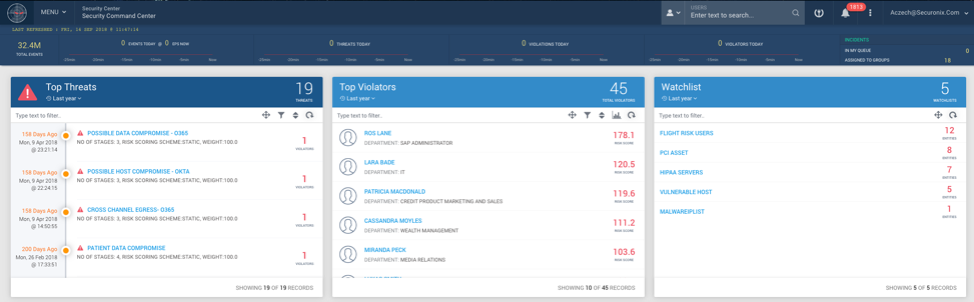
Securonix delivers a cloud-native SIEM platform that unifies threat detection, investigation, and response. The platform is built around analytics and AI, combining SIEM, UEBA, and SOAR capabilities. It runs on Snowflake’s data cloud and is designed to scale with large data volumes while reducing alert noise through curated threat content and behavioral analytics.
الميزات الرئيسية:
- Scalable data lake architecture: Provides access to up to one year of hot data for investigations and threat hunting, supporting large-scale log storage and fast search.
- Prebuilt threat content and analytics: Includes continuously curated detection content and analytics mapped to frameworks such as MITRE ATT&CK to reduce false positives and accelerate time to value.
- Integrated UEBA capabilities: Uses behavior analytics to monitor user and entity activity and detect insider threats and anomalous behavior.
- Embedded SOAR functionality: Supports automated workflows and response actions to reduce manual effort in incident handling.
- Cybersecurity mesh integration: Integrates with security tools, cloud platforms, and data lakes to centralize visibility across heterogeneous environments.

Source: Securonix
3. مايكروسوفت سنتينل

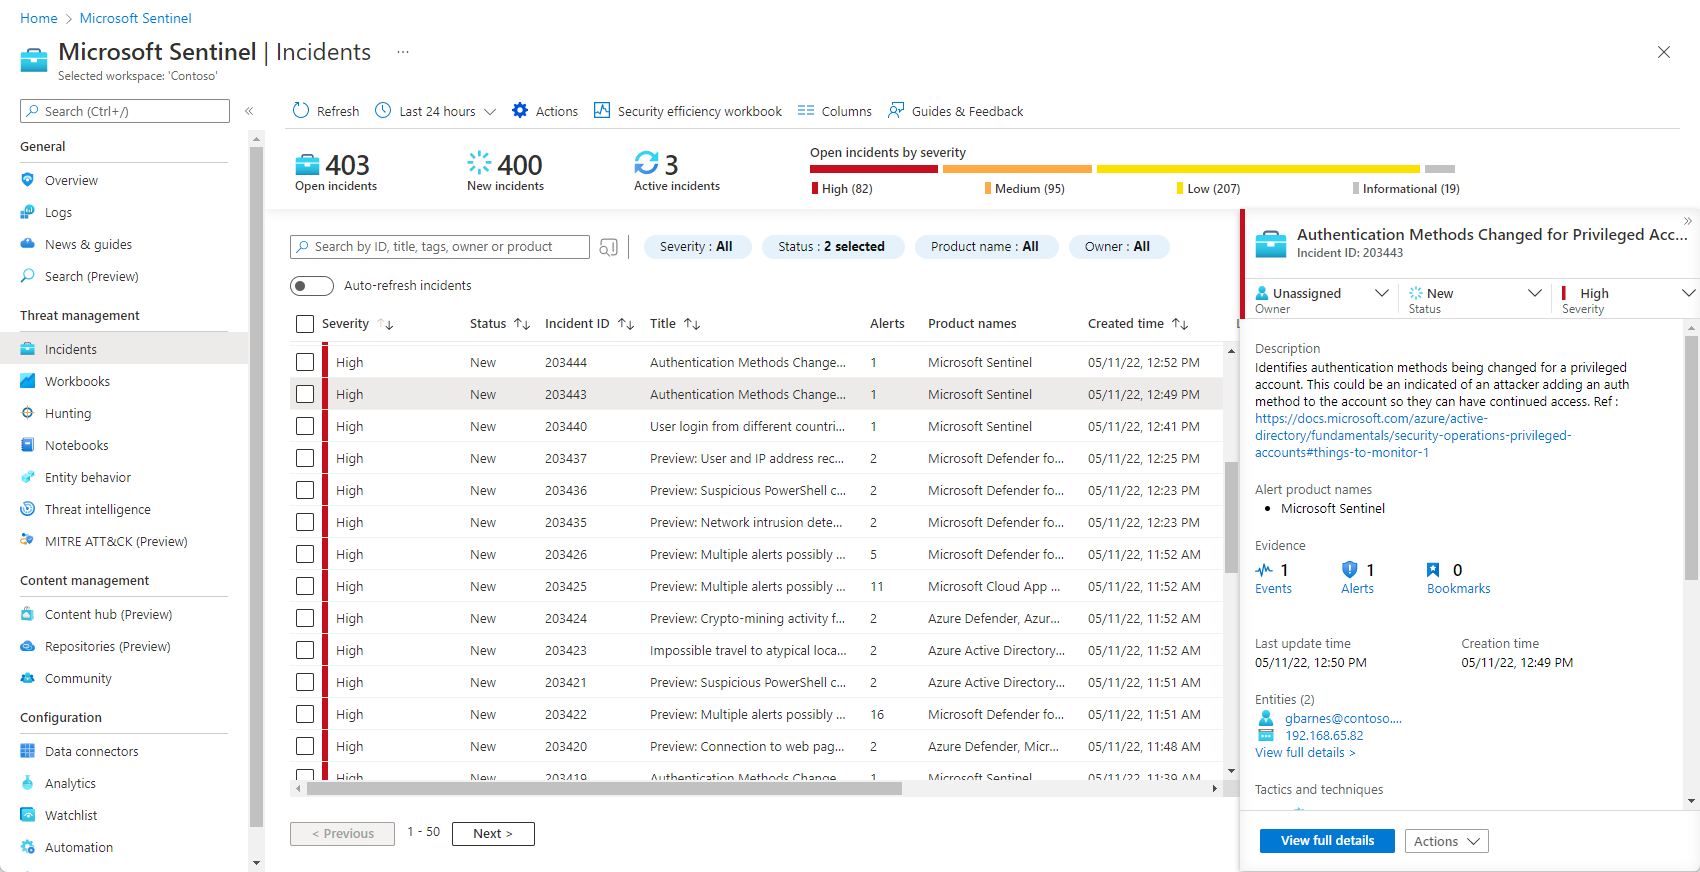
Microsoft Sentinel is a cloud-native SIEM platform that centralizes security data in a unified data lake and applies AI-driven analytics for detection and response. It integrates SIEM, SOAR, UEBA, and threat intelligence capabilities in a single platform. Sentinel supports multicloud and multiplatform environments through native connectors and built-in integrations.
- Cloud-native SIEM architecture: Combines SIEM capabilities with a scalable data lake for centralized storage and analytics.
- Built-in SOAR and UEBA: Includes native automation, user and entity behavior analytics, and threat intelligence without requiring separate add-ons.
- Extensive data connectors: Supports more than 350 built-in connectors and no-code custom integrations for Microsoft and non-Microsoft data sources.
- AI-powered investigation tools: Uses generative AI assistance to summarize incidents, generate queries, and recommend response actions to reduce investigation time.
- Native XDR integration: Integrates with Microsoft Defender to unify visibility and response across endpoints, identities, email, and cloud workloads.

Source: Microsoft
4. InsightIDR

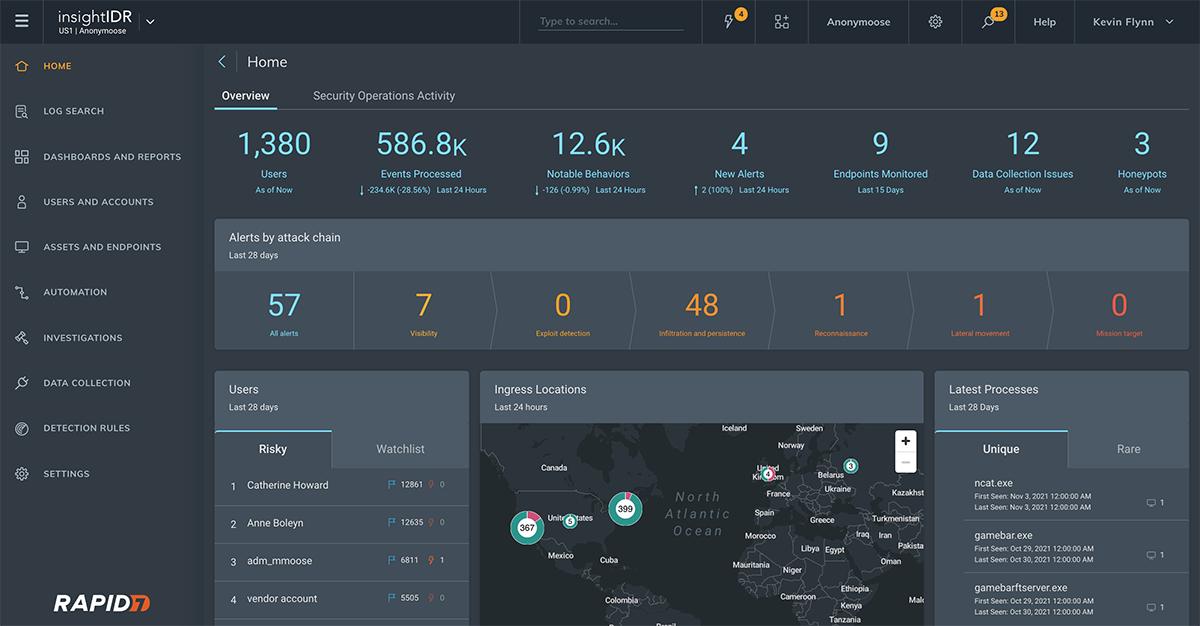
InsightIDR is a cloud-native SIEM and XDR platform delivered as a SaaS solution. It collects log, network, and endpoint data, normalizes it, and correlates user and asset activity to identify suspicious behavior. Data is gathered through on-premises collectors and endpoint agents, then analyzed in the cloud to provide centralized visibility and investigation workflows.
- Cloud-native SaaS deployment: Hosted in AWS with centralized analytics, reducing infrastructure management requirements.
- Integrated XDR capabilities: Combines log management, endpoint visibility, authentication monitoring, and network data for extended detection and response.
- User behavior analytics and correlation: Correlates users, accounts, authentications, and alerts to detect anomalous behavior and indicators of compromise.
- Built-in detection library: Provides vetted detection rules and embedded threat intelligence to accelerate deployment.
- Automated response workflows: Supports automation and response actions to contain threats and simplify investigations.

Source: Rapid7
Traditional SIEM Platforms
5. Splunk

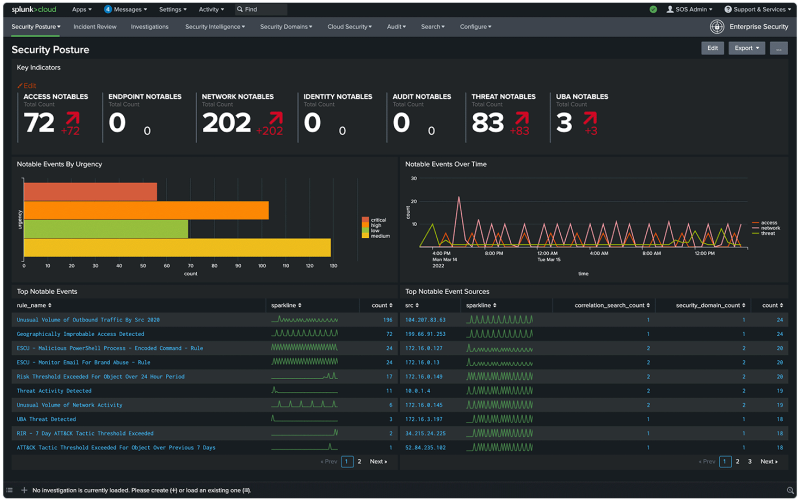
Splunk Enterprise Security is part of Splunk’s broader data platform, designed to ingest and analyze machine data at scale. It provides unified threat detection, investigation, and response capabilities, along with AI and automation features. The platform supports large-scale data ingestion from diverse sources and integrates with a wide ecosystem of applications and services.
- AI-native data platform: Enables real-time search, analysis, and action on machine data from multiple sources at enterprise scale.
- Unified threat detection and response: Delivers visibility, threat intelligence, and high-fidelity alerts within a consolidated security workflow.
- Extensive integration ecosystem: Supports thousands of integrations and add-ons for ingesting logs, metrics, traces, and events.
- Compliance monitoring capabilities: Automates compliance tracking and reporting for standards such as PCI, HIPAA, and GDPR.
- Built-in AI and machine learning: Uses machine learning and generative AI features to simplify workflows and enhance detection.

Source: Splunk
6. LogRhythm SIEM

LogRhythm SIEM is a self-hosted platform designed for organizations that require control over their deployment environment. It focuses on threat detection, investigation, and response (TDIR) by combining data collection, enrichment, correlation, and automated workflows. The platform contextualizes data at ingestion and provides out-of-the-box detection content mapped to industry frameworks.
- Machine data intelligence fabric: Enriches and translates log data at ingestion to make it usable for security analysis.
- Extensive correlation rules: Includes more than 1,100 prebuilt correlation rules, mapped to frameworks such as MITRE ATT&CK, with support for custom detections.
- Unified TDIR workflows: Provides investigation timelines, dashboards, and reporting within a single interface to simplify analyst workflows.
- Embedded SOAR capabilities: Offers automated response actions through built-in SmartResponse workflows to reduce manual effort.
- Self-hosted deployment model: Supports on-premises or self-managed private cloud deployments to meet data sovereignty and control requirements.
7. IBM QRadar SIEM

IBM QRadar SIEM centralizes security data to provide real-time threat detection and compliance reporting. It is designed to help analysts prioritize incidents, reduce false positives, and investigate threats more efficiently. The platform integrates with a range of security tools and supports analytics use cases such as insider threat detection and threat hunting.
- Real-time threat detection and correlation: Monitors and correlates data across environments to identify threats as they occur.
- User behavior analytics: Detects anomalous user activity and insider threats through built-in UBA capabilities.
- Sigma rule support: Incorporates open-source Sigma rules to strengthen detection coverage.
- Extensive integrations: Connects with numerous third-party tools and partner extensions for broad ecosystem visibility.
- Compliance and reporting support: Helps organizations demonstrate compliance with regulatory requirements through centralized logging and reporting.

Source: IBM
8. Trellix Security Platform

Trellix provides a broad security platform that integrates security operations across endpoint, network, email, data, and cloud environments. The platform uses generative and predictive AI to enhance detection and investigation workflows. It centralizes visibility and management through a single console, supporting hybrid and on-premises deployments.
- Integrated security platform: Unifies endpoint, network, data, email, cloud, and third-party security controls within one architecture.
- GenAI-powered analytics: Uses generative and predictive AI for detection, guided investigations, and alert summarization.
- Platform-wide correlation: Correlates data across security controls to improve threat visibility and prioritization.
- Threat hunting and case management: Provides dashboarding, case management, and hunting capabilities within a centralized console.
- Resilient deployment architecture: Supports on-premises, hybrid, cloud, and air-gapped environments.

Source: Trellix
9. LogPoint

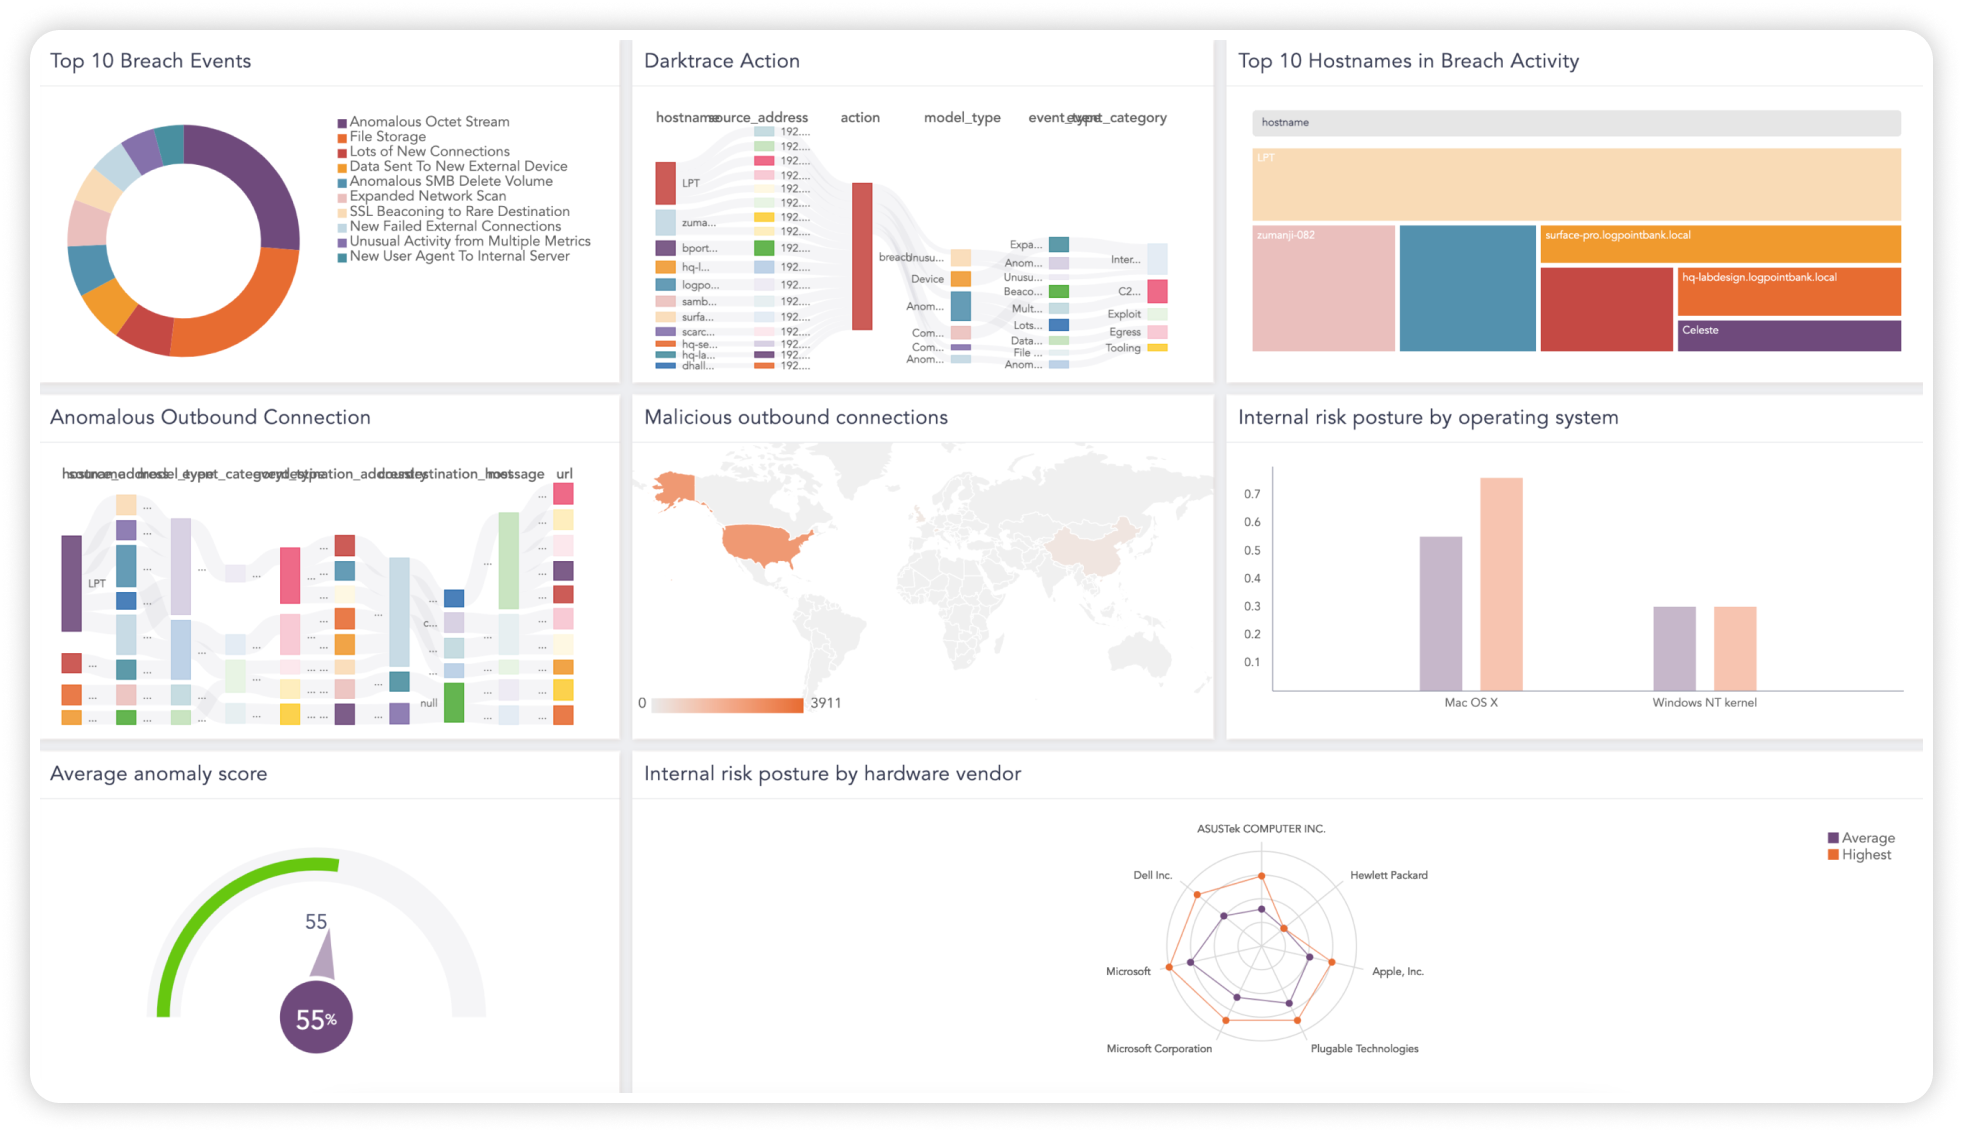
Logpoint delivers a SecOps platform that integrates SIEM, SOAR, and network detection and response capabilities. It is designed to provide centralized visibility and automation while supporting cloud, hybrid, and on-premises deployments. The platform emphasizes built-in detections and integration flexibility to reduce operational overhead.
- Integrated SecOps platform: Combines SIEM, SOAR, NDR, and centralized management in a single solution.
- Extensive built-in detections: Includes more than 1,000 preconfigured detections to reduce manual rule creation.
- Broad integration support: Supports over 100 integrations to connect security tools and data sources.
- Automation and response capabilities: Automates incident response processes to reduce analyst workload.
- Sovereign-ready deployment options: Supports cloud, hybrid, and on-premises environments to meet data residency requirements.

Source: LogPoint
10. Elastic Stack

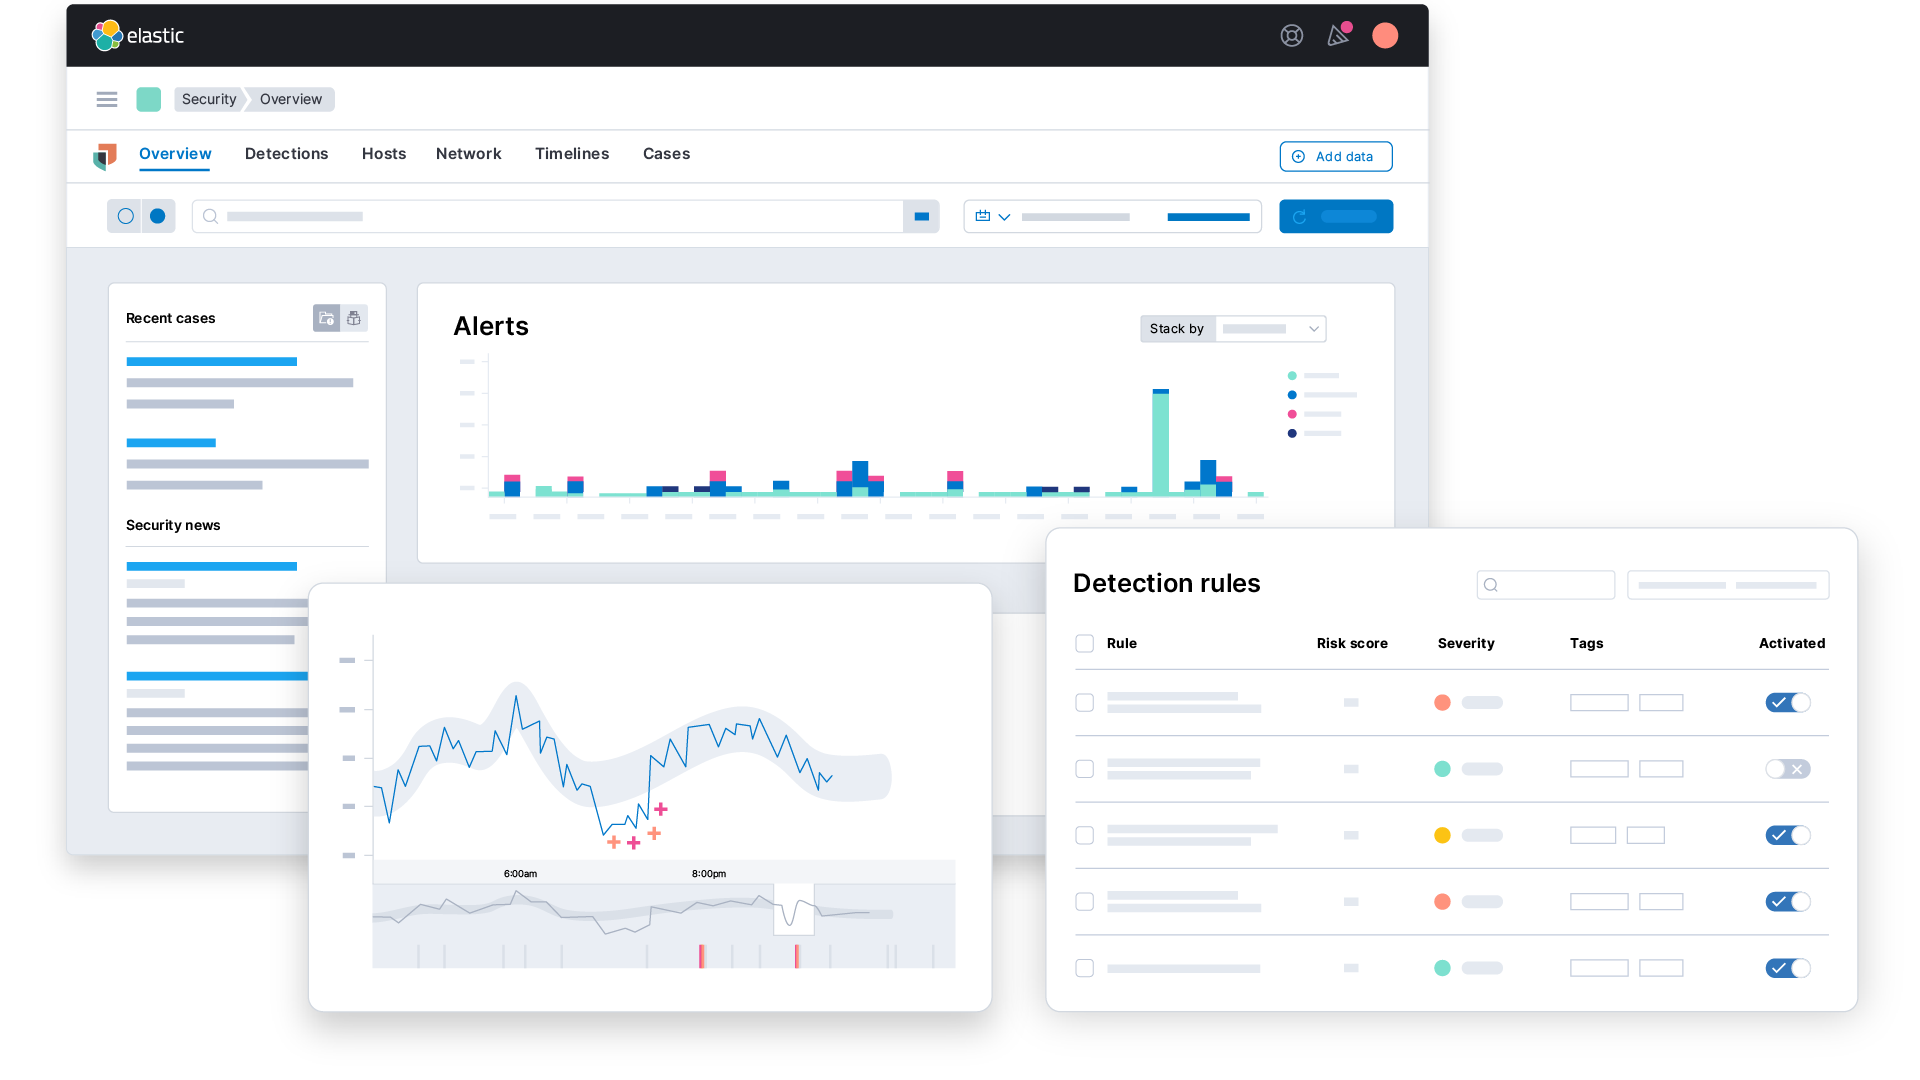
Elastic provides log analytics and observability capabilities built on Elasticsearch. It supports ingestion, indexing, and analysis of large volumes of structured and unstructured log data. The platform includes AI-driven log processing and supports open standards such as OpenTelemetry.
- Scalable log ingestion and storage: Handles large-scale log volumes with indexing, compression, and optimized storage mechanisms.
- AI-driven log parsing and structuring: Automatically parses and structures unstructured logs for easier analysis.
- Query engine (ES|QL): Supports filtering, correlation, aggregation, and transformation of log data.
- Agentic AI and machine learning: Surfaces significant events, generates queries, and assists with investigations using AI-driven capabilities.
- Open-source foundation: Built on Elasticsearch with OpenTelemetry support for standardized data collection and interoperability.

المصدر: إيلاستيك ستاك
11. ArcSight Enterprise Security Manager

OpenText Enterprise Security Manager (ArcSight ESM) is a SIEM platform that provides real-time threat detection, correlation, and automation. It combines comprehensive data collection with a native threat intelligence feed and built-in SOAR capabilities. The platform is designed to reduce alert volume and accelerate incident response.
- Correlation engine: Detects threat-correlated events in real time to reduce time to detect and respond.
- Native SOAR integration: Automates response workflows directly within the SIEM platform.
- Built-in threat intelligence feed: Enhances detection with integrated intelligence data.
- Data collection: Aggregates logs and events from across the environment for centralized analysis.
- Alert reduction capabilities: Minimizes duplicate and false-positive alerts to prioritize meaningful threats.

Source: ArcSight
كيفية اختيار مزود خدمة SIEM
جميع أنظمة SIEM التي ذكرناها أعلاه هي حلول قوية ولها قاعدة مستخدمين واسعة. عند اختيار نظام SIEM، قم بتقييم سجل البائع وموقعه في السوق، واهتم بشكل خاص بالوظائف.
فيما يلي نعرض القدرات الأساسية التي تحدد حل SIEM، والقدرات المتقدمة التي تضيف الذكاء والأتمتة، لجعل SIEM أكثر فعالية لمنظمتك. تغطي أفضل حلول SIEM القدرات الأساسية، وتضيف ميزات الجيل التالي المناسبة لاحتياجات الأمان الخاصة بك.
القدرات الأساسية لنظام إدارة معلومات الأمان
- كشف التهديدات– توفر أنظمة إدارة معلومات الأمان (SIEM) كشفًا دقيقًا للتهديدات بمساعدة القواعد وتحليلات السلوك. كما أنها تجمع معلومات التهديدات، والقوائم السوداء، والمواقع الجغرافية.
- معلومات التهديدات والتنبيه الأمني– العديد من أنظمة إدارة معلومات الأمان (SIEM) تربط نظام الأمان الخاص بك بتغذية معلومات التهديدات. هذا يضمن أن عملك محدث بأحدث التهديدات السيبرانية. كما تقوم أنظمة SIEM بتجميع وتطبيع بيانات الأمان الخاصة بك، والتحقق من مصادر مختلفة، وتقييم نشاط نظامك، وتنبيهك في أي وقت يكتشفون فيه حدثًا مشبوهًا.
- تقييم الامتثال والتقارير– الامتثال هو أحد أكبر العقبات التي تواجه أي عمل، وهو يزداد تعقيدًا. اللوائح مثل FFIEC وHIPAA وPCI، تحدد كيف وما البيانات التي يجب تخزينها. عدم الامتثال للمتطلبات التنظيمية يمكن أن يؤدي إلى نتائج كارثية للأعمال. توفر أنظمة SIEM تقارير الامتثال ويمكن أن تساعدك في تحديد فعالية عملك في تلبية المتطلبات التنظيمية.
- إشعارات فورية– عندما يتعلق الأمر بالأمان، فإن الوقت هو جوهر الأمر وستقوم أنظمة إدارة معلومات الأمان بإخطارك بأي خروقات أمنية في الوقت الحقيقي. وهذا يسمح لعملك بالاستجابة على الفور لأي تهديد محتمل.
- تجميع البيانات– إن مركزية المعلومات من العديد من المصادر وتوفير صورة واضحة عن جميع أنشطة شبكتك هي أهم ميزة في نظام SIEM. بدون ذلك، سيكون من السهل فقدان تتبع الزوايا المظلمة في شبكتك، خاصة مع نمو عملك. هذه الفجوة في الرؤية يستغلها المجرمون الإلكترونيون بسهولة، مما يترك شبكتك عرضة للاختراق غير المكتشف.
- توحيد البيانات– يتكون نظام الأمان الخاص بك من كميات هائلة من البيانات من مصادر مختلفة. لتحديد العلاقات في أحداث الأمان، يجب تنسيق كل هذه البيانات بشكل متسق. يقوم نظام SIEM بتوحيد جميع بيانات الأمان الخاصة بك، مما يسهل تحليلها واستخلاص استنتاجات ذات مغزى منها.
قدرات نظم إدارة معلومات الأمان من الجيل التالي
- جمع البيانات وإدارتها –يمكن لأنظمة SIEM الحديثة جمع وإدارة البيانات من جميع المصادر المتاحة، مع تسهيل التكامل من خلال الموصلات المدمجة. الأنواع المهمة من مصادر البيانات هي الموارد والخدمات السحابية، وبيانات الشبكة وبيانات السجلات المحلية، والأجهزة الخارجية مثل الهواتف الذكية.
- تسليم السحابة –تستفيد أنظمة SIEM السحابية من التخزين السحابي المرن وبحيرات البيانات. وهذا يجعلها أكثر قابلية للتوسع بكثير من أنظمة SIEM التقليدية الموجودة في الموقع، والتي تعتمد على معدات لا يمكنها التعامل مع الأحجام الضخمة من البيانات التي تنتجها المؤسسات الكبيرة.
- تحليل سلوك المستخدم والكيانات (UEBA) –يؤسس خط أساس لسلوك المستخدمين النموذجي ويستخدم خوارزميات التعلم الآلي لتحديد الشذوذ السلوكي. تمكن هذه التقنية أنظمة SIEM الحديثة من الكشف بفعالية عن التهديدات من نوع يوم الصفر والتهديدات الداخلية، التي لا تتوافق مع توقيعات الهجوم المعروفة.
- تنسيق الأمان واستجابة الأتمتة (SOAR) –يمكن أن تمكن أنظمة SIEM من الاستجابة للحوادث الأمنية عند حدوثها، بدلاً من مجرد المراقبة والتنبيه. يمكن لأنظمة SIEM من الجيل التالي التعاون مباشرة مع بنية تكنولوجيا المعلومات والبنية التحتية الأمنية، مما يجعل اقتراحات للإجراءات ذات الصلة. يمكنها أيضًا أتمتة استجابة التهديدات باستخدام كتيبات IR، وتنسيق أدوات الكشف عن التهديدات والاستجابة المستخدمة من قبل أنظمة متعددة، وإدارة أنظمة الأمان مثل جدران الحماية، وخوادم البريد الإلكتروني وإدارة الوصول.
- جداول زمنية للهجمات الآلية –تتطلب أنظمة SIEM التقليدية من المحللين جمع البيانات من مصادر مختلفة لفهم تسلسل الهجوم. يمكن أن يكون هذا مستهلكًا للوقت ويتطلب خبرة خاصة. يمكن لأنظمة SIEM من الجيل التالي بناء تسلسل الهجوم تلقائيًا وعرضه بصريًا حتى يتمكن المحللون الأقل تخصصًا من فهمه. وهذا يجعل التحقيق وتصنيف الحوادث أسرع بكثير.
استنتاج
مع تزايد الهجمات السيبرانية وارتفاع مستوى شهرتها، أصبح من المهم أكثر من أي وقت مضى فهم أدوات الأمن السيبراني المتاحة. عندما يتعلق الأمر بتقارير الأمان، هناك تضارب بين حجم البيانات والعملية. بينما لا ترغب في تفويت أي حدث أمني، فإن إدارة جميع التنبيهات من جميع الأنظمة في بنية الأمان الخاصة بك أمر مستحيل ببساطة.
هنا يأتي دور نظام SIEM. من خلال مركزية جميع الإشعارات في منصة واحدة، ستتلقى إشعارًا عن أي حدث يحتاج إلى انتباهك دون إضاعة الوقت في مراقبة أنظمة متعددة. لتحسين ملفك الأمني بشكل أكبر، يمكنك دمج SIEM مع حلول مثل SOAR وUEBA لأتمتة اكتشاف التهديدات، وتقليل الإيجابيات الكاذبة، والاستجابة للتهديدات، أو الاستثمار في عرض SIEM من الجيل التالي.
نصائح من الخبير

ستيف مور هو نائب الرئيس ورئيس استراتيجيات الأمن في إكزبيم، يساعد في تقديم الحلول لاكتشاف التهديدات وتقديم المشورة للعملاء بشأن برامج الأمن والاستجابة للاختراقات. وهو مضيف بودكاست "The New CISO Podcast"، و عضو في Forbes Tech Council، ومؤسس مشارك لـ TEN18 at Exabeam.
من خلال تجربتي، إليك بعض النصائح التي يمكن أن تساعدك في تحسين استخدامك وتعظيم إمكانيات حلول SIEM لعملك:
خطط لاحتياجات التخزين والاحتفاظ مسبقًا
قم بتقييم متطلبات الامتثال الخاصة بك والنمو المتوقع للبيانات. تأكد من أن استراتيجية تخزين SIEM الخاصة بك (محلية أو سحابية) يمكن أن تتعامل مع الاحتفاظ بالسجلات دون تدهور في الأداء.
ركز على العلاقات ذات المعنى، وليس فقط التنبيهات
خصص قواعد الترابط لإعطاء الأولوية للتنبيهات ذات التأثير الحقيقي في العالم. يمكن أن يؤدي الاعتماد المفرط على القواعد الجاهزة إلى إرهاق التنبيهات وفقدان الأحداث الحرجة.
دمج نظام إدارة معلومات الأمان (SIEM) مع أنظمة إدارة خدمات تكنولوجيا المعلومات (ITSM)
ربط نظام إدارة معلومات الأمان الخاص بك مع منصات إدارة خدمات تكنولوجيا المعلومات مثل ServiceNow يسهل إدارة الحوادث. يضمن هذا الدمج تسجيل التنبيهات كطلبات وتتبعها حتى الحل.
استفد من تدفقات معلومات التهديد المتقدمة
قم بتعزيز نظام إدارة معلومات الأمان الخاص بك بتدفقات معلومات التهديد الفاخرة في الوقت الحقيقي لتحسين قدرات الكشف ضد التهديدات الناشئة والهجمات المستهدفة.
قم بضبط وتحسين نماذج التعلم الآلي بانتظام في أنظمة SIEM من الجيل التالي
تأكد من أن ميزات الذكاء الاصطناعي وUEBA في نظام SIEM من الجيل التالي الخاص بك مضبوطة وفقًا لسلوك منظمتك. راجع نتائج النماذج بشكل دوري للتأكد من دقتها وملاءمتها.
تعلم المزيد عن إكزابييم
تعرف على منصة Exabeam ووسع معرفتك في أمن المعلومات من خلال مجموعتنا من الأوراق البيضاء، البودكاست، الندوات، والمزيد.