NDR Solutions: Key Features and 7 Tools to Know in 2026
- 8 minutes to read
فهرس المحتويات
ما هي حلول الكشف والاستجابة للشبكات (NDR)؟
حلول الكشف والاستجابة للشبكات (NDR) هي تقنيات أمن سيبراني تركز على تحديد التهديدات والتخفيف منها داخل الشبكة. توفر رؤية لحركة مرور الشبكة وتستخدم التحليلات لاكتشاف الأنشطة المشبوهة.
تساعد أدوات NDR في تحديد الشذوذ والانتهاكات الأمنية المحتملة، مما يوفر لفرق الأمن رؤى قابلة للتنفيذ للاستجابة بسرعة للتهديدات. من خلال المراقبة المستمرة لنشاطات الشبكة، تساعد هذه الحلول في ضمان وجود آليات دفاعية.
تستخدم حلول NDR مجموعة من التقنيات، بما في ذلك التعلم الآلي وتحليل السلوك، للكشف عن التهديدات في حركة المرور المشفرة وغير المشفرة. وهي تكمل تدابير الأمان الأخرى من خلال التركيز على الحركة الجانبية، والتهديدات الداخلية، والتهديدات المستمرة المتقدمة.
Editor’s note: Updated the article to cover recent market trends, updated product information to reflect features and capabilities in 2026.
Network Detection and Response Market Trends
The network detection and response market is steadily expanding. It has already reached USD 3.89 billion. By 2031, it is expected to grow to USD 5.59 billion, with a compound annual growth rate (CAGR) of 6.24%.
This growth is driven by a shift from reactive monitoring to proactive threat hunting. Organizations are investing in tools that provide continuous visibility and faster detection across complex environments.
Technology and Adoption Trends
AI-driven anomaly detection is gaining traction, with higher growth compared to traditional signature-based methods. Organizations are also focusing on monitoring encrypted east-west traffic, especially in operational technology (OT) environments.
There is a growing trend toward hybrid deployments. Companies process sensitive data on-premises while using cloud analytics for scalability and efficiency.
Managed security service providers (MSSPs) are packaging NDR into bundled services. This makes advanced detection accessible to smaller organizations without in-house expertise.
Challenges and Constraints
False positives remain a major issue. Security teams often spend significant time investigating benign alerts, reducing overall efficiency.
Data residency regulations limit cloud adoption in some regions. Organizations must balance compliance with the benefits of cloud-based NDR.
There is also a shortage of skilled cybersecurity professionals. This gap increases reliance on automation and external service providers.
ما هي فوائد برنامج NDR؟
استخدام حل NDR يوفر للمنظمات الفوائد التالية.
تعزيز الدفاع الأمني
تعزز حلول NDR الدفاعات الأمنية من خلال مراقبة الأنشطة الشبكية بشكل مستمر لتحديد التهديدات المحتملة. تستخدم التحليلات لفحص كميات كبيرة من بيانات الشبكة، مع الإشارة إلى أي شذوذ قد يدل على مشكلة أمنية. يساعد ذلك في منع خروقات البيانات المتعلقة بالشبكة من خلال التعرف على الأنشطة الضارة مبكرًا.
الرؤية العميقة
من خلال التقاط وتحليل بيانات الشبكة الدقيقة، تقدم هذه الأدوات رؤية شاملة للأنشطة الشبكية. هذه الرؤية تمكن فرق الأمان من فهم الأنماط الطبيعية للشبكة واكتشاف الانحرافات التي قد تشير إلى مشكلات أمنية. تضمن تحليلات البيانات التي تقدمها أدوات NDR اكتشاف التهديدات الدقيقة ومعالجتها بسرعة.
البحث عن التهديدات والاستجابة لها بشكل أسرع
تسرع حلول NDR من عمليات البحث عن التهديدات من خلال تزويد فرق الأمان ببيانات دقيقة وقابلة للتنفيذ. كما أنها تقلل من الضوضاء عن طريق تصفية الأنشطة غير الضارة، مما يسمح للمحللين بالتركيز على التهديدات الحقيقية. هذه القدرة تبسط عملية تحديد التهديدات والتخفيف منها، مما يقلل من إمكانية الأضرار الناتجة عن الحوادث السيبرانية.
الميزات الرئيسية لأدوات NDR
التنبيهات الفورية والاستجابة للحوادث
من خلال المراقبة المستمرة وقدرات الكشف السريع، تولد هذه الأدوات تنبيهات بمجرد ملاحظة أنشطة مشبوهة. تتيح هذه الإشعارات الفورية للفرق تحديد الأولويات ومعالجة التهديدات قبل أن تتسبب في أضرار كبيرة.
تُسرع استجابة الحوادث أيضًا من خلال آليات الاستجابة الآلية في حلول NDR. يمكن لهذه الأنظمة اتخاذ إجراءات محددة مسبقًا عند اكتشاف التهديدات، مثل عزل الأجهزة المتأثرة أو حظر حركة المرور الضارة.
فحص الحزم العميق (DPI)
يعزز فحص الحزم العميق أدوات الكشف عن التهديدات الشبكية من خلال تمكين تحليل مفصل لحزم البيانات التي تعبر الشبكة. يقوم فحص الحزم العميق بفحص كل من رأس الحزمة ومحتواها، مما يوفر رؤية دقيقة لحركة المرور ويساعد في تحديد الأنماط الخبيثة التي قد تفوتها طرق الفحص الأبسط.
يوفر هذا الفحص طبقة إضافية من الأمان من خلال تحديد التهديدات المراوغة، بما في ذلك تلك المخفية داخل حركة المرور المشفرة. يسمح استخدام الفحص العميق للحزم (DPI) لحلول الكشف عن التهديدات (NDR) بتحديد وحجب التهديدات التي قد تغفلها أدوات الأمان التقليدية. من خلال تحليل محتوى الحزم، يمكن لـ DPI اكتشاف والاستجابة للتهديدات مثل البرمجيات الخبيثة، ومحاولات التسلل، وتسريب البيانات.
تحليل حركة المرور المشفرة
يسمح تحليل حركة المرور المشفرة بتحليل تدفقات البيانات المشفرة دون الحاجة إلى فك تشفير الحركة، مما يحافظ على سرية البيانات مع اكتشاف الأنشطة الضارة. يحدد تحليل حركة المرور المشفرة الشذوذ مثل طول الجلسات غير المعتاد أو أنماط الاتصال، والتي قد تشير إلى وجود تهديد.
مع ETA، تضمن حلول NDR أن استخدام التشفير لا يتحول إلى نقطة عمياء في اكتشاف التهديدات. من خلال تقديم رؤى حول حركة المرور المشفرة، تحافظ أدوات NDR على تدابير الأمان دون المساس بخصوصية وسرية الحركة التي تحللها.
التحقيقات الشبكية
يساعد التحليل الجنائي للشبكات في فهم النطاق الكامل وتأثير الحوادث الأمنية. من خلال الاحتفاظ بسجلات الأنشطة الشبكية، تدعم أدوات NDR التحقيقات بعد الحوادث. يمكن للمحللين تتبع طرق الهجوم، وتحديد الأنظمة المتضررة، وفهم تكتيكات الخصوم، مما يحسن الدفاعات المستقبلية ويساعد في ملاحقة الفاعلين الخبيثين.
توفر حلول NDR المزودة بقدرات تحليل الشبكات غوصًا عميقًا في كيفية حدوث الاختراقات، مما يساعد على تحديد الثغرات أو نقاط الضعف في الشبكة. تضمن القدرة على تدقيق الأنشطة بدقة أن يتم دمج أي دروس مستفادة في استراتيجيات الأمن السيبراني، مما يعزز المنظمة ضد التهديدات المحتملة في المستقبل.
دعم البيئات السحابية والهجينة
مع انتقال المنظمات إلى البيئات السحابية والهجينة، تطورت حلول NDR لدعم هذه الهياكل. فهي توفر رؤية شاملة عبر الشبكات المحلية والسحابية والهجينة، مما يضمن تنفيذ سياسات الأمان بشكل متسق. يساعد ذلك في الحفاظ على موقف أمني موحد، بغض النظر عن مكان وجود البنية التحتية.
مع دعم البيئات السحابية والهجينة، تعالج أدوات NDR التحديات المنفصلة التي تطرحها هذه الإعدادات، مثل التوسع الديناميكي والأحمال المرنة. تمكّن حلول NDR المؤسسات من اكتشاف التهديدات عبر بيئات متنوعة، مما يضمن أن تظل تدابير الأمان متماشية مع التقدم التكنولوجي والتغيرات في البنية التحتية.
اقرأ شرحنا المفصل حول صيد التهديدات.
نصائح من الخبير

ستيف مور هو نائب الرئيس ورئيس استراتيجيات الأمن في إكزبيم، يساعد في تقديم الحلول لاكتشاف التهديدات وتقديم المشورة للعملاء بشأن برامج الأمن والاستجابة للاختراقات. وهو مضيف بودكاست "The New CISO Podcast"، و عضو في Forbes Tech Council، ومؤسس مشارك لـ TEN18 at Exabeam.
من خلال تجربتي، إليك بعض النصائح التي يمكن أن تساعدك في الاستفادة بشكل أفضل من حلول NDR:
استغلال تدفقات معلومات التهديد: قم بتعزيز قدرات NDR باستخدام تدفقات معلومات التهديد الخارجية لتحديد التهديدات المستمرة المتقدمة (APTs) وهجمات اليوم الصفري التي يصعب اكتشافها باستخدام بيانات الشبكة فقط.
ضبط نماذج التعلم الآلي بانتظام: يمكن أن تولد حلول NDR التي تعتمد على الذكاء الاصطناعي والتعلم الآلي ضوضاء إذا لم يتم ضبطها بشكل صحيح. قم بتحسين النماذج بانتظام باستخدام بيانات محددة للبيئة وتعليقات لتقليل الإيجابيات الكاذبة وتحسين دقة الكشف.
تنفيذ تقسيم الشبكة: استخدم NDR بالاشتراك مع تقسيم الشبكة لعزل المناطق الحساسة. من خلال تقليل سطح الهجوم، يصبح من الأسهل احتواء أي شذوذ يتم اكتشافه، وتتحسن أوقات الاستجابة بشكل كبير.
ربط NDR مع بيانات النقاط النهائية وSIEM: قم بمقارنة اكتشافات NDR مع أدوات اكتشاف النقاط النهائية والاستجابة (EDR) أو أدوات SIEM. يعزز هذا الربط الرؤية ويمكن أن يساعد في تحديد الأسباب الجذرية بشكل أكثر فعالية عبر أسطح الهجوم.
تشفير مراقبة حركة المرور شرق-غرب: بينما تركز العديد من أدوات الكشف عن التهديدات على حركة المرور شمال-جنوب، لا تتجاهل حركة المرور الداخلية شرق-غرب داخل شبكتك. تأكد من أن أداة الكشف عن التهديدات الخاصة بك يمكنها التعامل مع الاتصالات الداخلية المشفرة أو نشر حلول تحلل حركة المرور المشفرة بفعالية.
حلول NDR الملحوظة
AI-Driven / Proprietary NDR Platforms
1. أريستا NDR
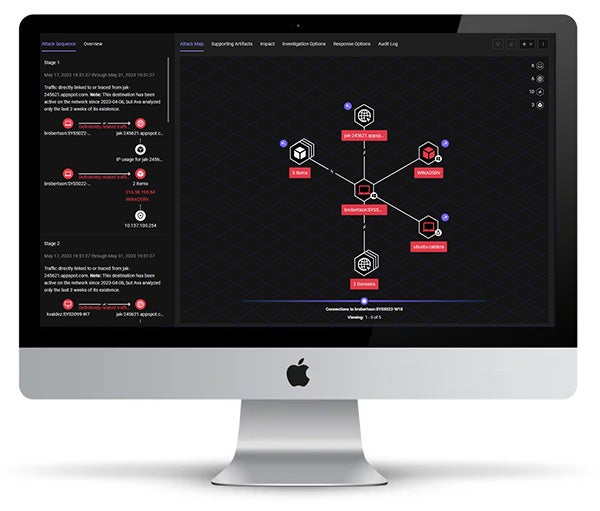
Arista NDR is a network detection and response platform to provide continuous visibility and analysis across enterprise environments. It focuses on identifying abnormal behavior and malicious intent by analyzing relationships between users, devices, and applications, supporting faster investigation and response.
الميزات الرئيسية لـ Arista NDR تشمل:
- Continuous network visibility: Monitors all users, devices, and applications to provide a complete view of the attack surface.
- Behavioral analytics and anomaly detection: Learns patterns across entities and detects deviations that may indicate threats.
- Automated threat investigation: Correlates evidence over time to build context and visualize attack chains across entities and protocols.
- Threat hunting and custom detection models: Supports automated threat hunting and allows teams to define models for specific risks.
- Context-rich forensics and timelines: Provides detailed evidence and timelines to support incident analysis and response.
- Integration with existing tools: Shares insights with other security and IT systems to extend detection and response workflows.

2. تحليلات الشبكة الآمنة من سيسكو
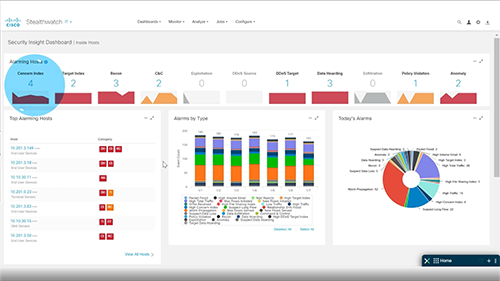
Cisco Secure Network Analytics is an NDR solution that analyzes network telemetry to detect threats that bypass traditional defenses. It uses behavioral modeling and analytics to identify suspicious activity across network environments, including encrypted traffic.
تشمل الميزات الرئيسية لتحليلات الشبكة الآمنة من سيسكو ما يلي:
- Behavioral modeling and machine learning: Establishes baselines of normal activity and detects anomalies indicating potential threats.
- Real-time threat detection with context: Generates alerts enriched with details such as user, device, and application context.
- Encrypted traffic analytics: Identifies threats within encrypted traffic without requiring decryption.
- Detection of insider threats and unknown attacks: Helps uncover data exfiltration, policy violations, and previously unseen threats.
- Policy validation and compliance monitoring: Evaluates and improves network policies while supporting investigations.
- Integration with XDR and security tools: Connects with Cisco XDR and other systems for coordinated detection and response.

3. Darktrace DETECT
Darktrace DETECT is an AI-driven NDR solution that uses self-learning algorithms to understand normal behavior across an organization and identify deviations. It focuses on detecting novel and evolving threats without relying on predefined signatures.
تشمل الميزات الرئيسية لـ Darktrace DETECT ما يلي:
- Self-learning AI models: Continuously learns normal patterns across users, devices, and systems to detect anomalies.
- Detection of unknown threats: Identifies subtle deviations and previously unseen attack techniques, including novel malware.
- Continuous real-time monitoring: Analyzes multiple metrics across the environment to uncover emerging threats.
- Automated investigation with AI analyst: Uses AI to investigate alerts, correlate events, and generate incident summaries.
- Noise reduction and prioritization: Consolidates multiple alerts into a smaller set of high-priority incidents.
- Integration with automated response: Feeds detections into response systems to enable rapid mitigation.

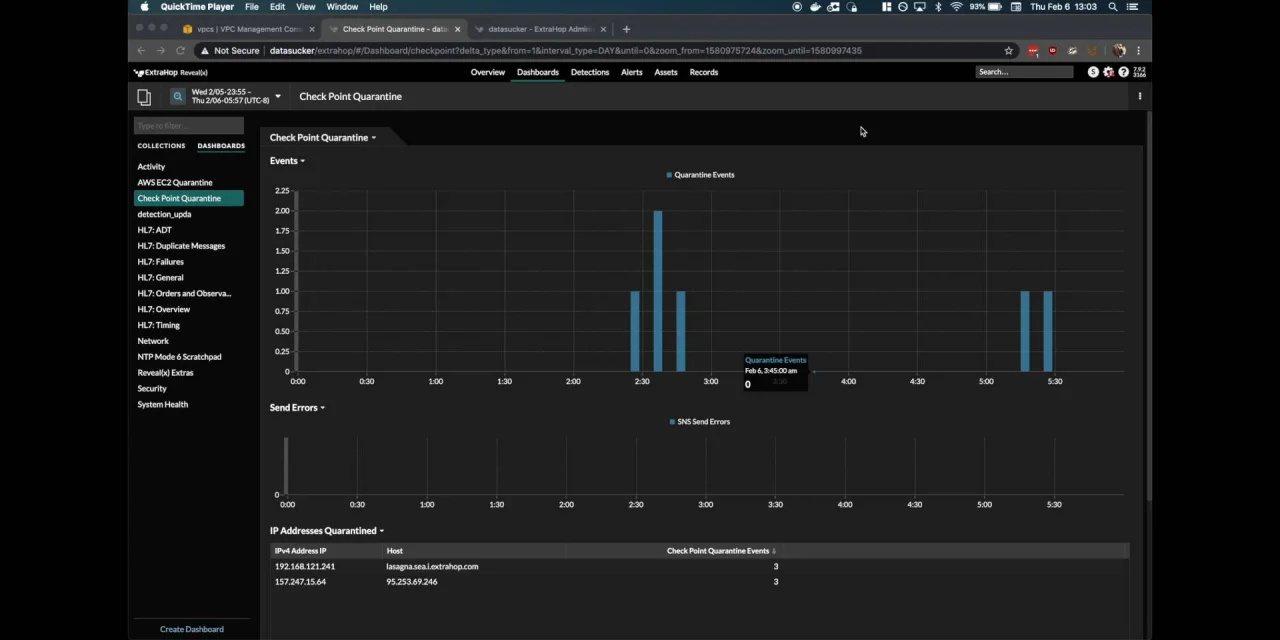
4. ExtraHop RevealX
ExtraHop RevealX is an NDR platform that provides visibility and analysis of network traffic across on-premises and cloud environments. It combines packet analysis, machine learning, and automation to detect threats and support investigations.
تشمل الميزات الرئيسية لبرنامج ExtraHop RevealX ما يلي:
- Network visibility: Captures and analyzes traffic across on-premises, cloud, and hybrid environments.
- Deep packet and protocol analysis: Decodes and analyzes protocols to extract detailed insights from network traffic.
- Automatic asset discovery and profiling: Continuously identifies and profiles devices, users, and applications on the network.
- AI-driven anomaly detection: Uses machine learning to baseline behavior and detect unusual activity.
- Integrated network forensics: Supports investigation with stored traffic data and contextual metrics.
- Workflow automation and integrations: Connects with SIEM, EDR, and SOAR tools and automates investigation steps.

5. Corelight Open NDR
Corelight Open NDR is a platform that combines open-source and proprietary technologies to deliver network detection and response capabilities. It focuses on providing deep visibility, flexible integrations, and multiple detection methods within a unified system.
تشمل الميزات الرئيسية لـ Corelight Open NDR ما يلي:
- Open-source powered detection: Leverages technologies like Zeek and Suricata for network monitoring and analysis.
- Unified detection approaches: Combines machine learning, behavioral analytics, and signature-based methods.
- Packet capture and evidence correlation: Links alerts with packet data to provide detailed investigation context.
- Integrated threat intelligence: Enriches detections with external and internal threat intelligence sources.
- SOC workflow automation: Supports integration with SIEM, XDR, and SOAR platforms for automated response.
- Flexible and extensible architecture: Enables customization and integration through an open ecosystem.

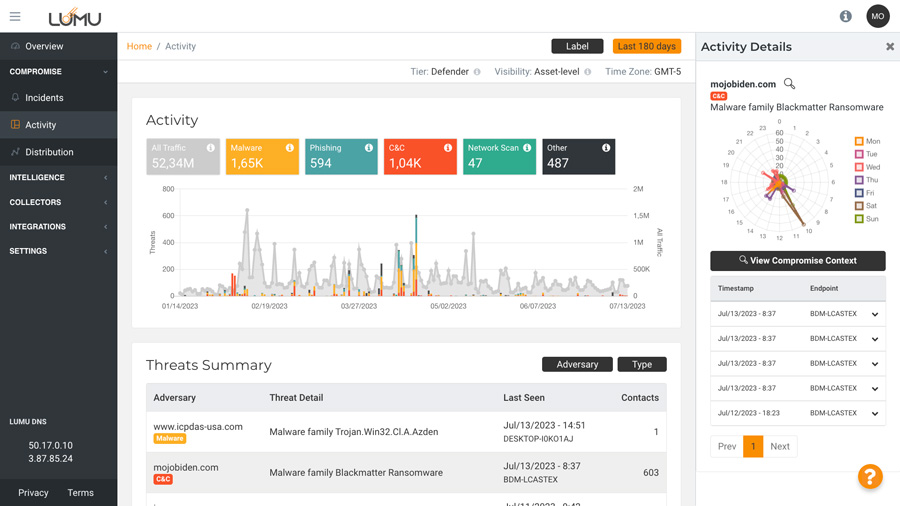
6. Lumu NDR
Lumu NDR is a threat detection and response platform that focuses on continuous compromise detection across network, endpoint, and cloud environments. It integrates with existing security tools to automate detection and response workflows.
الميزات الرئيسية لـ Lumu NDR تشمل:
- Continuous compromise monitoring: Tracks network activity to identify indicators of compromise in real time.
- Unified visibility across environments: Provides insight into network, endpoint, identity, and cloud activity.
- Automated response through integrations: Connects with existing security tools to trigger response actions automatically.
- Detection of threats bypassing defenses: Identifies attacks that evade traditional security controls.
- Contextual threat insights: Provides actionable information to support timely investigation and response.
- Seamless ecosystem integration: Integrates with a wide range of third-party security platforms.

7. Verizon Network Detection and Response
Verizon Network Detection and Response is a cloud-delivered NDR platform that combines traffic capture, analytics, and response capabilities. It focuses on providing full network visibility and long-term forensics to support proactive threat detection and investigation.
تشمل الميزات الرئيسية لخدمة Verizon NDR ما يلي:
- Cloud-delivered architecture: Enables deployment across enterprise, cloud, and industrial environments without specialized hardware.
- Full-packet capture and retention: Stores network traffic for detailed forensic analysis and retrospective threat hunting.
- Advanced detection techniques: Uses machine learning, behavioral analytics, and threat intelligence to identify threats.
- Integrated detection and response workflows: Correlates events and supports automated response and remediation.
- Long-term searchable forensics: Allows teams to investigate past activity and validate exposure to new threats.
- Scalable data processing and analytics: Handles large volumes of network data with elastic compute and storage.

قدرات منصة Exabeam: SIEM، UEBA، SOAR، التهديدات الداخلية، الامتثال، TDIR
تطبق منصة عمليات الأمن من Exabeam الذكاء الاصطناعي والأتمتة على سير عمل عمليات الأمن من أجل نهج شامل لمكافحة التهديدات السيبرانية، مما يوفر أكثر طرق الكشف عن التهديدات والتحقيق فيها والاستجابة لها فعالية.
- تحدد الاكتشافات المدفوعة بالذكاء الاصطناعي التهديدات عالية المخاطر من خلال تعلم السلوك الطبيعي للمستخدمين والكيانات، وإعطاء الأولوية للتهديدات باستخدام تقييم مخاطر يعتمد على السياق.
- تُبَسِّط التحقيقات الآلية عمليات الأمان، حيث تربط البيانات المتباينة لإنشاء جداول زمنية للتهديدات.
- تقوم الوثائق (Playbooks) بتنظيم سير العمل والمعايير لتسريع التحقيق والاستجابة.
- تقوم التصورات برسم التغطية مقابل النتائج الاستراتيجية الأكثر أهمية والأطر اللازمة لسد الفجوات في البيانات والكشف.
مع هذه القدرات، تمكّن Exabeam فرق العمليات الأمنية من تحقيق TDIR بشكل أسرع وأكثر دقة وثباتًا.
استكشاف منصة عمليات الأمن من Exabeam.
تعلم المزيد عن إكزابييم
تعرف على منصة Exabeam ووسع معرفتك في أمن المعلومات من خلال مجموعتنا من الأوراق البيضاء، البودكاست، الندوات، والمزيد.