


فهرس المحتويات
ما هي منصة SOAR؟
A تنسيق الأمن والأتمتة والاستجابة platform simplifies security operations through a combination of people, processes, and technology. Its main objective is to improve efficiency by automating repetitive tasks and supporting coordinated incident response.
يساعد هذا التكامل فرق الأمان على إدارة التهديدات بشكل أفضل من خلال الاستفادة المثلى من البيانات والعمليات الموجودة. تدعم منصات SOAR اتخاذ القرارات السريعة في بيئات الأمان المعقدة. كما أنها تتكامل مع أدوات متنوعة، مما يوسع من قدرة المؤسسة على اكتشاف التهديدات وتحليلها والاستجابة لها.
نشأت الحاجة إلى منصات SOAR نتيجة الزيادة المتزايدة في حجم التنبيهات، مما يتطلب معالجة أكثر كفاءة مما تسمح به العمليات اليدوية. تساعد الأتمتة في تقليل العمل اليدوي المتعلق بإدارة الحوادث وتمكين فرق الأمان من التركيز على مهام أكثر استباقية واستراتيجية. كما تدعم منصات SOAR التواصل والتقارير من خلال مركزية البيانات وتقديم رؤية موحدة للتهديدات والاستجابات.
Editor’s note: Updated the article to cover recent market trends, updated product information to reflect features and capabilities in 2026.
The SOAR Market Trends
The SOAR market is valued at USD 1.87 billion and is projected to reach USD 4.42 billion by 2030, growing at a CAGR of 18.82%. This growth reflects increasing demand for automated security operations as organizations handle rising alert volumes and more complex threat environments.
تسارع عدة عوامل عملية التبني:
- The surge in cyber incidents and alert volume is pushing teams toward automation to reduce manual triage. At the same time, a global shortage of cybersecurity professionals is forcing organizations to rely on platforms that can handle routine tasks.
- Regulatory pressure is also increasing. Compliance frameworks now require faster detection, response, and auditability, which SOAR platforms help deliver. In addition, cyber-insurance incentives encourage organizations to adopt automated response capabilities to reduce premiums.
Technology trends shaping SOAR include:
- Generative AI: It enables faster creation of playbooks and more adaptive response workflows. AI-assisted systems can reduce investigation time and increase the percentage of incidents resolved automatically.
- Cloud-first architectures: These platforms provide scalability, faster updates, and better integration across distributed systems. Another trend is the move toward composable SOCs, where API-driven tools are combined into flexible security stacks.
Market segmentation insights:
- Software platforms dominate the market, accounting for 64% of share. However, services are growing quickly as organizations need help with implementation and ongoing management.
- Cloud deployments lead with 71% market share and continue to expand due to their flexibility and alignment with Zero Trust models. Large enterprises still generate most revenue, but small and medium-sized businesses show the fastest growth due to increasing accessibility of SaaS-based solutions.
- By industry, banking and financial services lead adoption, while healthcare is emerging as the fastest-growing sector due to increased digitization and regulatory pressure.
الميزات الرئيسية لأدوات SOAR
إدارة الحوادث
تقوم أدوات SOAR بأتمتة جمع المعلومات السياقية المتعلقة بالحادث، مما يقلل من الوقت الذي يقضيه المحللون في جمع البيانات يدويًا. توفر هذه الوظيفة رؤى تفصيلية لكل حادث، مما يسمح بتقييم واستجابة أسرع. من خلال سير العمل الآلي، تقوم منصة SOAR بتصعيد القضايا الحرجة بسرعة، مما يمكّن الإدارة والفرق المعنية من اتخاذ الإجراءات بسرعة.
دليل الإجراءات وأتمتة سير العمل
من خلال كتب اللعب المحددة مسبقًا، تقوم أدوات SOAR بأتمتة المهام الروتينية، مما يضمن اتخاذ إجراءات متسقة في سيناريوهات التهديد المحددة. تقلل هذه الأتمتة من الأخطاء البشرية وتحرر موظفي الأمن للتعامل مع القضايا الأكثر تعقيدًا التي تتطلب تدخلًا بشريًا. من خلال توفير إطار عمل للتهديدات الشائعة، تتيح الأتمتة استجابات سريعة وفعالة.
دمج استخبارات التهديد
تقوم منصات SOAR بجمع معلومات التهديدات من مصادر متنوعة وتربطها بالبيانات الداخلية، مما يوفر رؤية شاملة للمخاطر المحتملة. يساعد هذا النهج في تحديد أولويات التهديدات بناءً على شدتها، مما يمكّن من اتخاذ ردود فعل حاسمة ومستنيرة. من خلال ربط معلومات التهديدات في الوقت الحقيقي مع سير العمل الآلي، تمكّن أدوات SOAR من التخفيف الاستباقي من التهديدات.
إدارة الحالات
تقدم أدوات SOAR ميزات إدارة الحالات التي تجمع بيانات الحوادث ذات الصلة، مما يسهل التحليل والتصنيف. يتم توثيق التفاصيل بشكل منهجي، مما يوفر منظورًا تاريخيًا كاملاً عن الحوادث الفردية والتهديدات المستمرة. تعزز هذه الرؤية الشاملة الوعي بالوضع واتخاذ القرار، مما يسمح لفرق الأمن بتخصيص الموارد.
التكامل مع أدوات SIEM وأدوات الأمان الأخرى
يمكن أن تتكامل هذه الأدوات مع SIEM (إدارة معلومات الأمن والأحداث) وأدوات الأمان الأخرى لتوسيع وظائفها. وهذا يمكّن المؤسسات من اكتشاف الشذوذ والاستجابة للحوادث من خلال ربط كميات هائلة من البيانات من مصادر مختلفة. تدعم منصات SOAR أيضًا التكامل مع أدوات الأمان الإضافية مثل جدران الحماية، وحماية النقاط النهائية، وأدوات فحص الثغرات.
محتوى ذو صلة: اقرأ دليلنا عنSIEM مقابل SOAR
نصائح من الخبير

ستيف مور هو نائب الرئيس ورئيس استراتيجيات الأمن في إكزبيم، يساعد في تقديم الحلول لاكتشاف التهديدات وتقديم المشورة للعملاء بشأن برامج الأمن والاستجابة للاختراقات. وهو مضيف بودكاست "The New CISO Podcast"، و عضو في Forbes Tech Council، ومؤسس مشارك لـ TEN18 at Exabeam.
من خلال تجربتي، إليك نصائح يمكن أن تساعدك في الاستفادة بشكل أفضل من منصة SOAR:
- أتمتة تصنيف التنبيهات بناءً على الخطورة: خصص منصتك SOAR لأتمتة تصنيف التنبيهات بناءً على مستويات الخطورة. هذا يقلل من إرهاق المحللين ويسمح للحوادث عالية الخطورة بتلقي اهتمام فوري، بينما يمكن التعامل مع التهديدات ذات المستوى الأدنى بتدخل minimal.
- الدمج مع أدوات إدارة خدمات تكنولوجيا المعلومات: ربط SOAR مع منصات إدارة خدمات تكنولوجيا المعلومات مثل ServiceNow يعزز التعاون بين فرق تكنولوجيا المعلومات والأمن. إنه يبسط معالجة الحوادث، مما يضمن توافق الأحداث الأمنية مع العمليات الأوسع لتكنولوجيا المعلومات من أجل حلول أسرع.
- استخدم أتمتة صيد التهديدات: استخدم SOAR لأتمتة أنشطة صيد التهديدات الاستباقية من خلال إعداد كتب اللعب التي تفحص مؤشرات معينة من التهديدات (IOCs) أو سلوكيات غير عادية بشكل مستمر، مما يحرر الموارد للتحليل الأعمق.
- مسارات التصعيد القابلة للتخصيص: إنشاء سير عمل تصعيد مرنة ضمن كتيبات اللعب الخاصة بك في SOAR تتكيف بناءً على نوع وتعقيد الحوادث. هذا يضمن توجيه التهديدات الحرجة إلى المحللين الكبار، بينما يمكن أتمتة الأحداث ذات الأولوية المنخفضة أو التعامل معها من قبل الموظفين المبتدئين.
- دمج تحليلات سلوك المستخدم (UBA): قم بتحسين اكتشاف الحوادث في نظام SOAR الخاص بك من خلال دمج UBA لمراقبة الشذوذ في سلوك المستخدم، مثل أوقات تسجيل الدخول غير العادية أو طلبات الوصول. يساعد ذلك في الكشف عن التهديدات الداخلية والحسابات المخترقة بشكل أسرع.
منصات وحلول SOAR البارزة
1. إكزابييم

إكزابييم هي مزود رائد لحلول إدارة معلومات وأحداث الأمان (SIEM)، تجمع بين UEBA وSIEM وSOAR وTDIR لتسريع عمليات الأمان. تمكّن منصات العمليات الأمنية الخاصة بها الفرق الأمنية من اكتشاف التهديدات والتحقيق فيها والاستجابة لها بسرعة، مع تعزيز الكفاءة التشغيلية.
الميزات الرئيسية:
- جمع السجلات وإدارتها القابلة للتوسع: تسرع المنصة المفتوحة عملية إدخال السجلات بنسبة 70%، مما يلغي الحاجة لمهارات هندسية متقدمة مع ضمان تجميع سلس للسجلات عبر البيئات الهجينة.
- تحليلات سلوكية: تستخدم تحليلات متقدمة لتحديد السلوك الطبيعي مقابل السلوك غير الطبيعي، وكشف التهديدات الداخلية، والحركة الجانبية، والهجمات المتقدمة التي تفوتها الأنظمة المعتمدة على التوقيع. يذكر العملاء أن Exabeam يساعد في الكشف والاستجابة لـ 90% من الهجمات قبل أن تتمكن الشركات الأخرى من اكتشافها.
- استجابة التهديدات الآلية: تبسط عمليات الأمان من خلال أتمتة جداول الحوادث، وتقليل الجهد اليدوي بنسبة 30%، وتسريع أوقات التحقيق بنسبة 80%.
- تحقيق الحوادث السياقية: نظرًا لأن Exabeam يقوم بأتمتة إنشاء الجداول الزمنية ويقلل من الوقت المستغرق في المهام البسيطة، فإنه يقلل من الوقت اللازم لاكتشاف التهديدات والاستجابة لها بأكثر من 50%. تقلل قواعد الكورليشن المسبقة البناء، ونماذج اكتشاف الشذوذ، ودمج البائعين من التنبيهات بنسبة 60%، مما يقلل من الإيجابيات الكاذبة.
- خيارات SaaS والسحابة الأصلية: توفر خيارات النشر المرنة قابلية التوسع للبيئات السحابية والهجينة، مما يضمن سرعة تحقيق القيمة للعملاء. بالنسبة للمنظمات التي لا تستطيع، أو لا ترغب في نقل SIEM الخاص بها إلى السحابة، تقدم Exabeam SIEM رائد في السوق، كامل الميزات، ومُستضاف ذاتيًا.
- رؤية الشبكة مع NetMon: يوفر رؤى عميقة تتجاوز الجدران النارية وأنظمة كشف التسلل/أنظمة منع التسلل، ويكتشف التهديدات مثل سرقة البيانات ونشاط الشبكات الآلية، مما يسهل التحقيق من خلال البحث المرن. كما أن تحليل الحزم العميق (DPA) يبني أيضًا على محرك فحص الحزم العميق (DPI) الخاص بـ NetMon لتفسير مؤشرات الاختراق الرئيسية (IOCs).
يبرز عملاء Exabeam باستمرار كيف أن رؤيتها في الوقت الحقيقي، والأتمتة، وأدوات الإنتاجية المدعومة بالذكاء الاصطناعي، تعزز من مهارات الأمن، وتحول المحللين المرهقين إلى مدافعين نشطين مع تقليل التكاليف والحفاظ على دعم رائد في الصناعة. لمزيد من المعلومات قم بزيارة Exabeam.com
2. سبلك SOAR

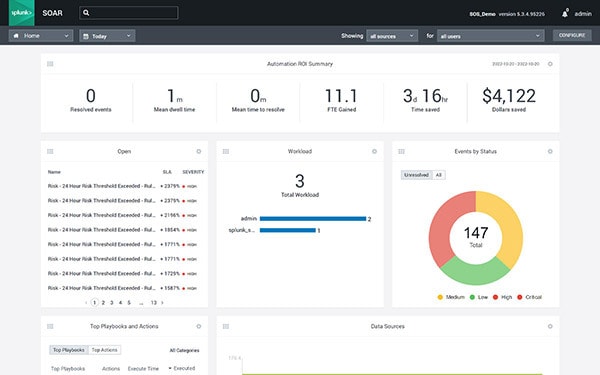
Splunk SOAR is a security orchestration and automation platform that connects security tools and coordinates workflows across the SOC. It enables teams to automate incident response processes and manage alerts from multiple systems in a centralized environment. The platform integrates with existing security stacks and supports both manual and automated investigation workflows.
الميزات الرئيسية لـ Splunk SOAR:
- Automated playbooks: Executes predefined workflows to automate response actions across tools.
- Extensive integrations: Connects with over 300 third-party tools and supports thousands of automated actions.
- Visual playbook editor: Provides a low-code interface for building and customizing workflows.
- Centralized case management: Organizes tasks, evidence, and collaboration during investigations.
- Threat intelligence support: Enriches investigations with built-in research and contextual insights.
- Workflow orchestration: Coordinates processes across multiple tools without replacing existing systems.
- Flexible deployment: Supports cloud, on-premises, and hybrid environments.

3. Google Security Operations SOAR

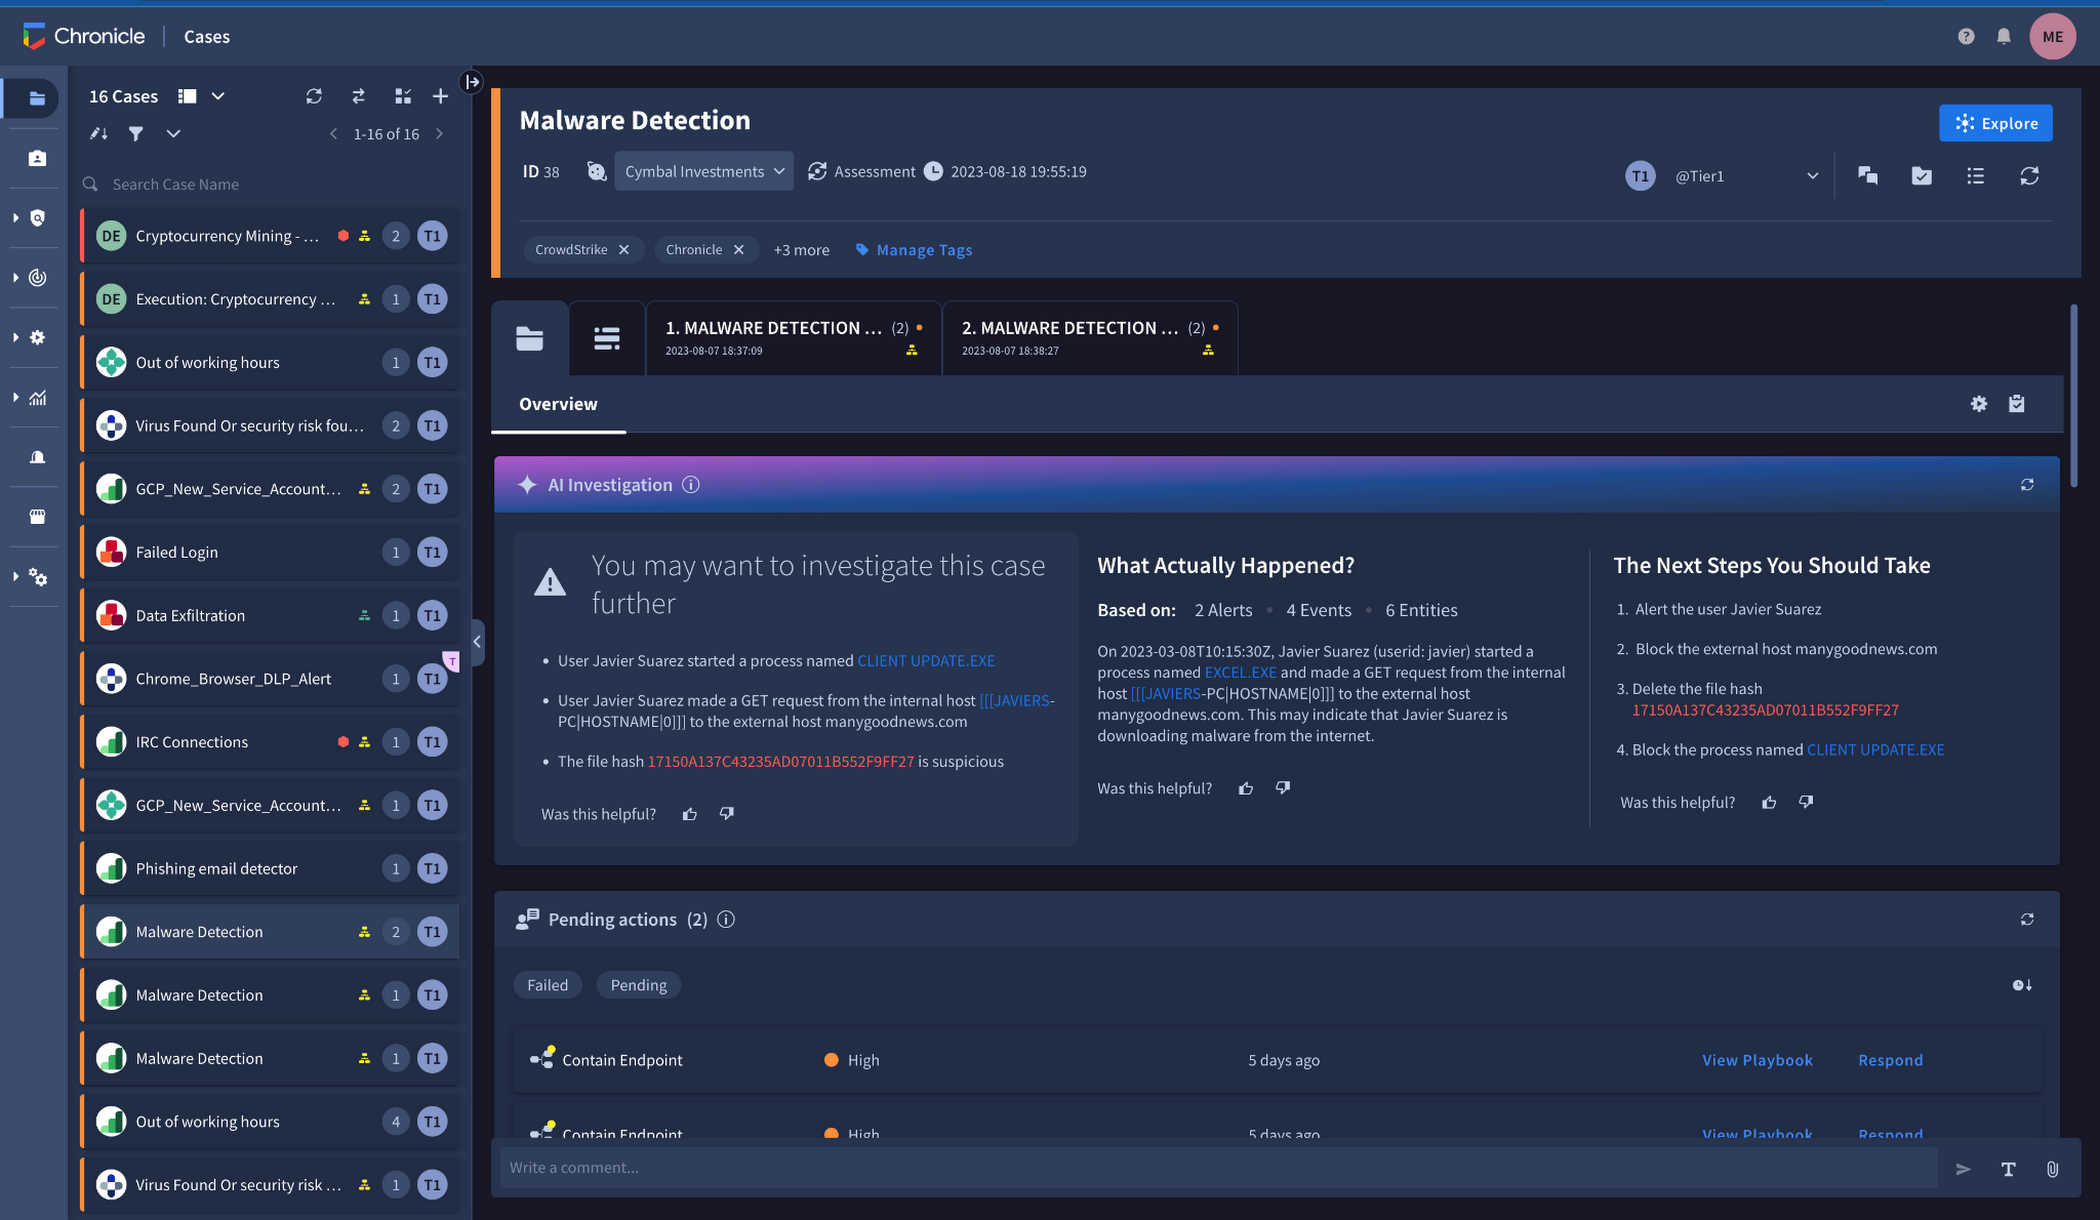
Google Security Operations SOAR is an automation platform built on Google Cloud that serves as a central execution layer for security workflows. It enables organizations to collect data from multiple sources, automate response actions, and integrate tools into a unified operational environment. The platform focuses on reducing manual effort and accelerating investigation and response processes.
الميزات الرئيسية لعمليات الأمن في جوجل SOAR:
- Centralized workflow execution: Acts as a hub for orchestrating security processes across tools.
- Unified data ingestion: Collects and normalizes data from endpoints, networks, and threat intelligence sources.
- Playbook-driven automation: Automates complex response workflows using a built-in playbook engine.
- Integration with security tools: Connects with SIEM, vulnerability scanners, and other systems.
- Code-driven customization: Allows engineers to build and extend automation logic.
- Reduced manual effort: Automates repetitive tasks to speed up investigations.
- Cloud-native architecture: Runs on Google Cloud for scalability and flexibility.

4. IBM QRadar SOAR

IBM QRadar SOAR is a platform that helps to standardize and automate incident response processes while improving decision-making in the SOC. It uses automation for correlation, enrichment, and prioritization of incidents, helping teams respond faster and reduce manual workload.
الميزات الرئيسية لمنتج IBM QRadar SOAR:
- Dynamic playbooks: Adapts workflows in real time as incidents evolve.
- Automated incident enrichment: Adds context through correlation and threat intelligence.
- Case management: Tracks incidents across their full lifecycle with structured workflows.
- Playbook designer: Provides an interface for building and modifying response workflows.
- Response orchestration: Coordinates actions across integrated tools and processes.
- Regulatory support: Helps manage response processes aligned with privacy and breach regulations.
- Reduced response time: Automates investigation and prioritization tasks.


5. Palo Alto Networks Cortex XSOAR

Cortex XSOAR is a SOAR platform focused on automating incident response and orchestrating security operations across tools and teams. It centralizes incident data, integrates threat intelligence, and enables collaboration through a unified interface. The platform emphasizes reducing manual work and accelerating investigation workflows.
الميزات الرئيسية لـ Cortex XSOAR:
- Extensive integrations: Supports hundreds of integrations and automation packs across security tools.
- Playbook automation: Enables creation of automated workflows using a visual editor.
- Centralized incident workspace: Provides a shared environment for investigation, collaboration, and reporting.
- Integrated threat intelligence: Combines indicators and context within incident workflows.
- Automation of repetitive tasks: Reduces manual effort in triage and response.
- Orchestration across SOC: Connects people, processes, and tools into coordinated workflows.
- Prebuilt content packs: Offers ready-to-use automation for common security use cases.
6. فورتينت فورتيسوار

Fortinet FortiSOAR is a SOAR platform that centralizes incident management and automates security operations across IT and OT environments. It acts as a hub for coordinating workflows, integrating tools, and enforcing standardized response processes. The platform supports both enterprise and managed service use cases.
الميزات الرئيسية لمنتج FortiSOAR:
- Centralized incident management: Consolidates alerts and workflows into a single operational hub.
- Extensive integrations: Supports hundreds of integrations across multi-vendor environments.
- Prebuilt playbooks: Provides thousands of workflows for common security use cases.
- AI-assisted operations: Uses AI to guide investigations and automate tasks.
- Low-code playbook creation: Enables drag-and-drop workflow development.
- Built-in threat intelligence: Enriches investigations with global and external intelligence sources.
- Flexible deployment options: Supports SaaS, on-premises, and cloud-hosted deployments.


7. رابيد7 إنسايت كونكت

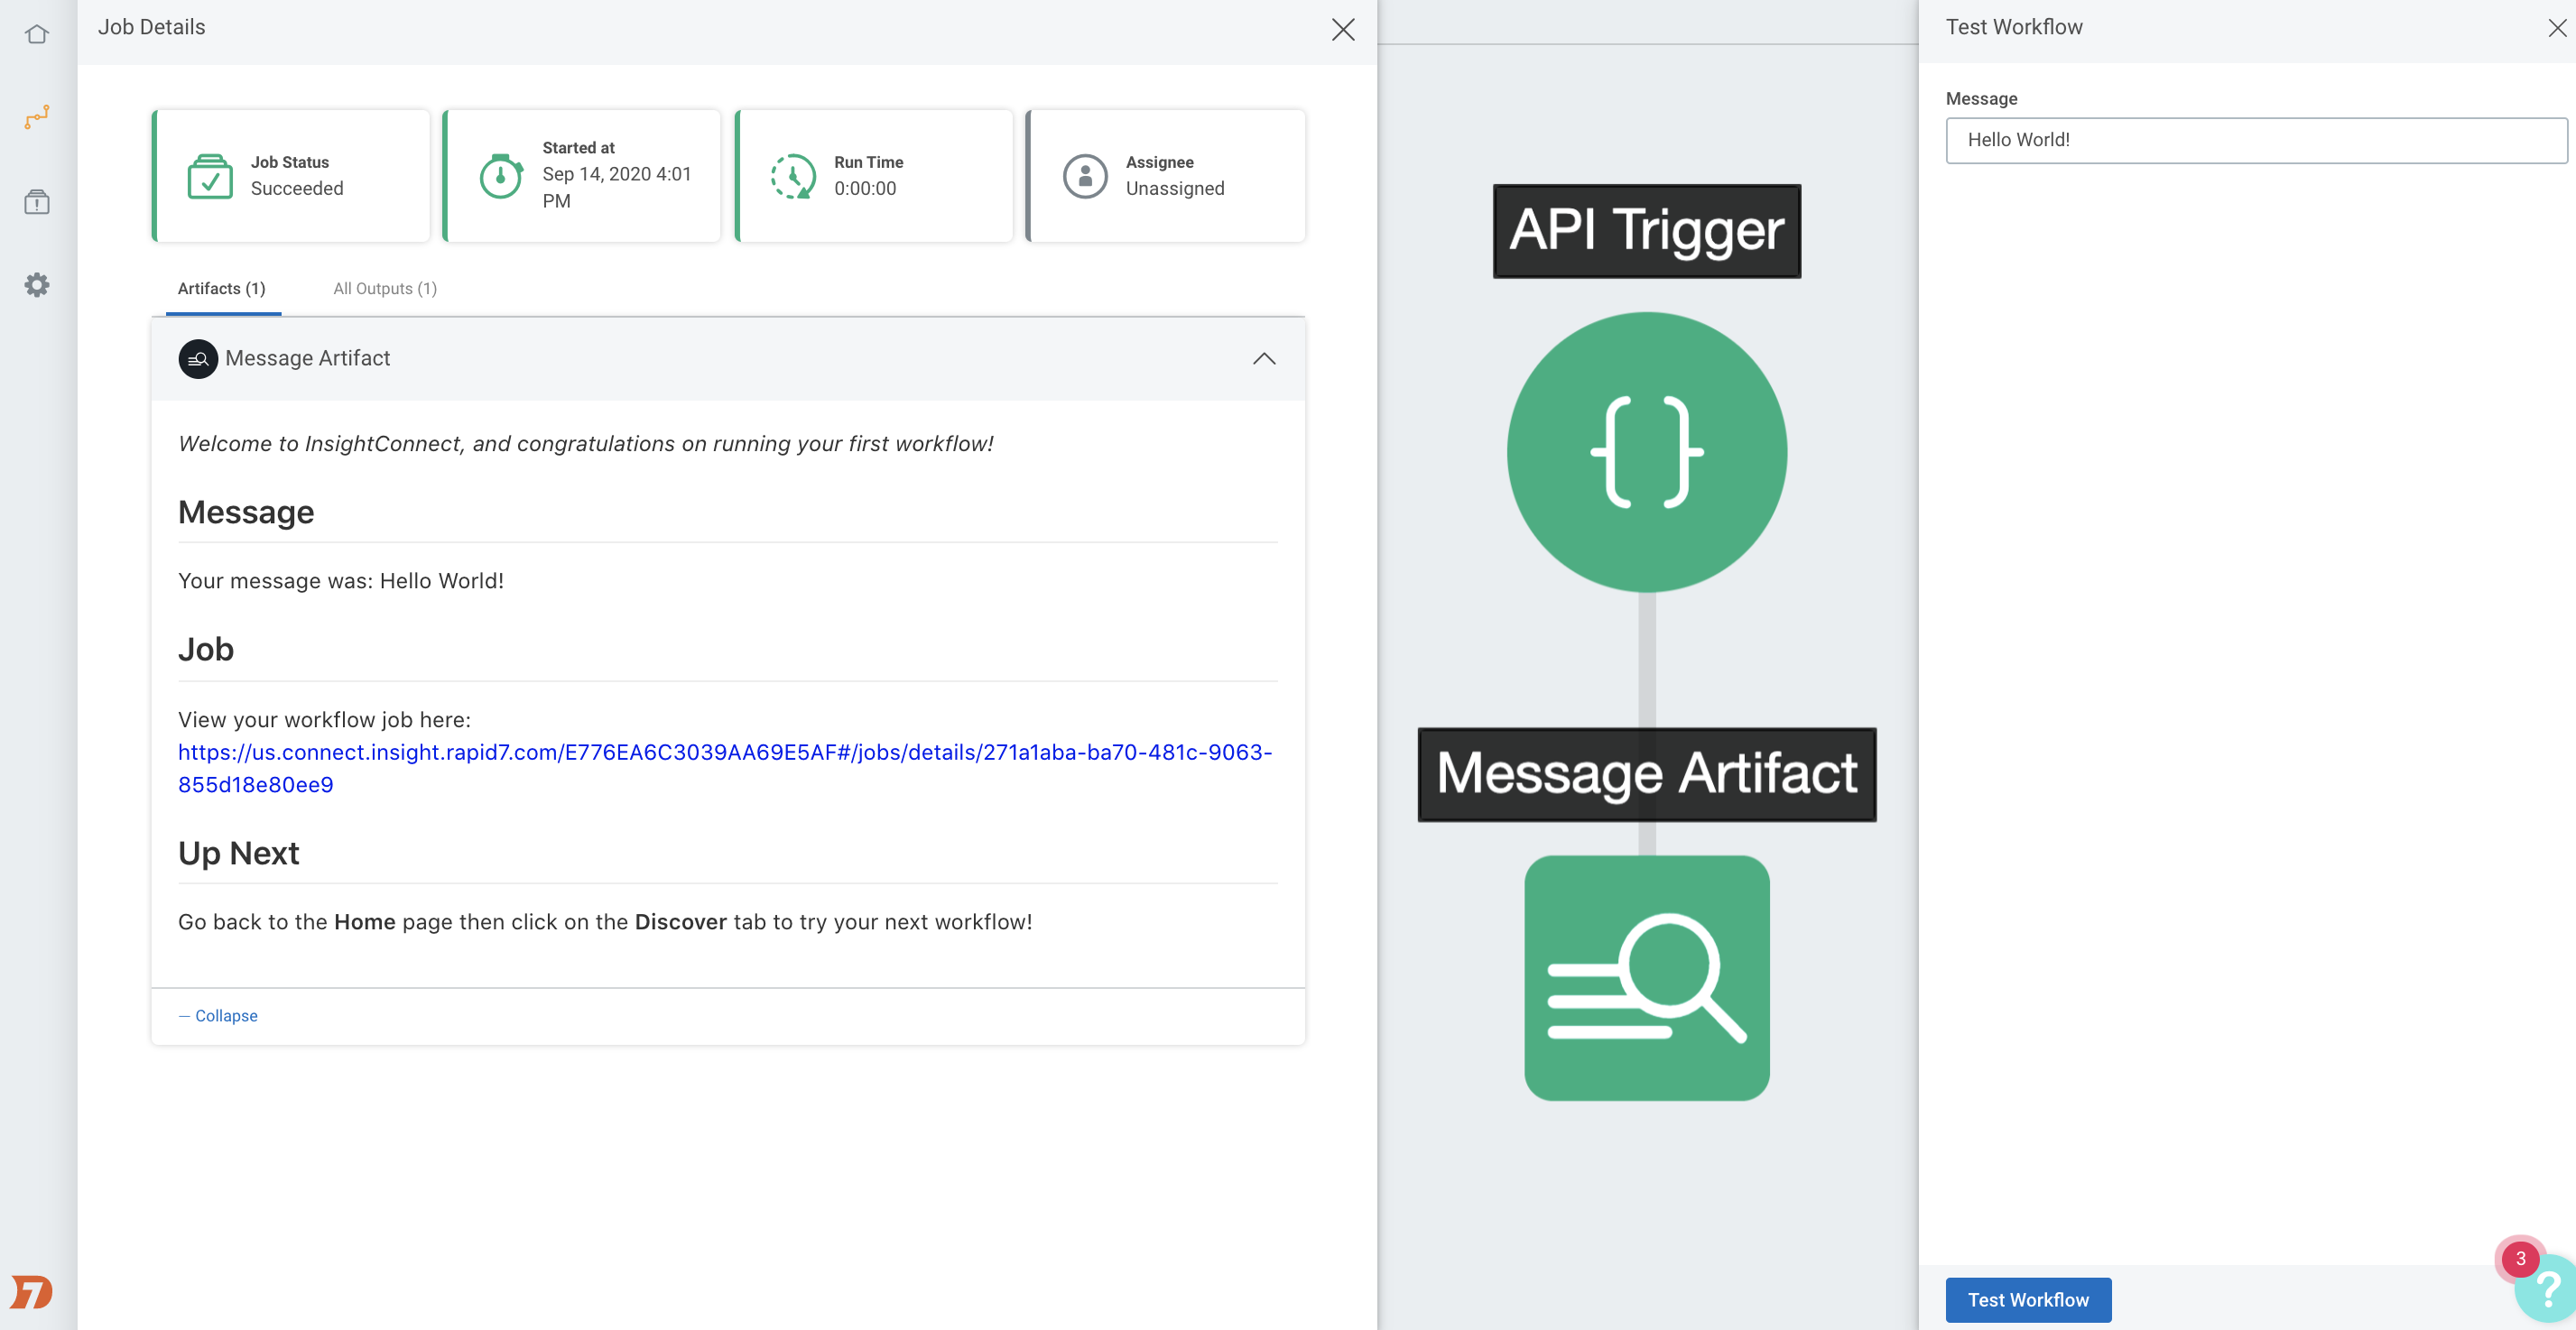
Rapid7 InsightConnect is a SOAR solution focused on workflow automation across security and IT tools. It enables teams to design automated processes that integrate multiple systems and reduce manual effort in incident response. The platform emphasizes usability with a no-code interface and predefined integrations.
الميزات الرئيسية لـ InsightConnect:
- Workflow automation engine: Automates security processes using triggers, steps, and reusable components.
- No-code workflow builder: Allows users to create automation without extensive coding.
- Extensive plugin ecosystem: Integrates with hundreds of tools and services.
- Cross-tool orchestration: Connects cloud apps, on-prem systems, and security tools.
- Human-in-the-loop controls: Supports manual approval steps within automated workflows.
- Reusable workflow components: Enables modular automation design.
- Audit and reporting support: Captures workflow data for analysis and compliance.

8. ساي وير

Cyware provides a SOAR platform focused on threat intelligence-driven automation and orchestration. It integrates intelligence collection, analysis, sharing, and response into a unified system, enabling organizations to act on threat data in real time and coordinate response across teams and partners.
الميزات الرئيسية لـ Cyware:
- Threat intelligence management: Ingests, enriches, and operationalizes intelligence from multiple sources.
- Automated response workflows: Uses AI-powered playbooks for rapid threat mitigation.
- Hyper-orchestration: Coordinates actions across tools and environments.
- Collaboration capabilities: Enables sharing of intelligence across teams and external partners.
- AI-driven analysis: Applies AI to improve detection and response decisions.
- Scalable integrations: Supports hundreds of integrations across security ecosystems.
- Real-time threat actioning: Enables immediate response based on intelligence insights.

9. ديفو سوار

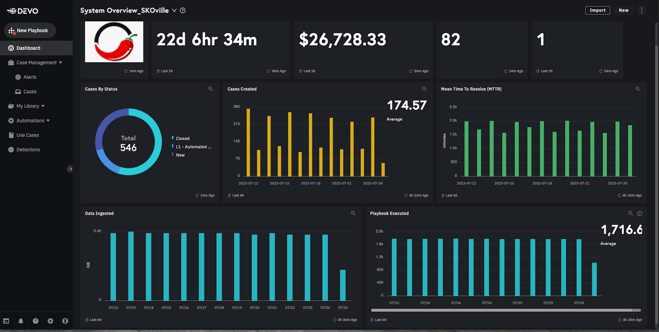
Devo SOAR is a cloud-native SOAR solution that helps improve SOC efficiency through automation and AI-driven workflows. It integrates with a broader security data platform to support real-time detection, investigation, and response.
الميزات الرئيسية لـ Devo SOAR:
- Cloud-native architecture: Delivered as a SaaS platform for scalability.
- Automated case management: Handles incident workflows and investigation processes.
- AI-driven automation: Uses intelligent automation to support decision-making.
- Integration with security data platform: Connects detection, analysis, and response.
- Support for threat hunting: Enables proactive investigation workflows.
- Real-time operations: Processes and responds to threats as they occur.
- Improved SOC efficiency: Reduces manual workload through automation.

10. ممر السباحة

Swimlane is a SOAR platform focused on automation and orchestration using AI and low-code workflows. It enables security teams to automate processes across a range of use cases, from incident response to compliance and vulnerability management.
الميزات الرئيسية لـ Swimlane:
- Low-code playbook automation: Enables rapid creation and modification of workflows.
- AI-powered automation: Uses AI agents to assist with investigations and responses.
- Extensive integrations: Connects with a wide range of security and IT tools.
- Case management and reporting: Tracks incidents and provides operational insights.
- Agentic AI capabilities: Supports dynamic decision-making within workflows.
- Automation across use cases: Extends beyond SOC to compliance and risk management.
- Centralized orchestration platform: Coordinates actions across the security environment.


استنتاج
أصبحت منصات SOAR ضرورية في عمليات الأمان الحديثة، حيث توفر للمنظمات القدرة على أتمتة وتبسيط سير العمل في الاستجابة للحوادث. من خلال التكامل مع البنية التحتية الأمنية الحالية، تساعد هذه المنصات الفرق الأمنية على إدارة كميات متزايدة من التنبيهات بكفاءة، وتقليل أوقات الاستجابة، وتحسين اتخاذ القرارات.
تعلم المزيد عن إكزابييم
تعرف على منصة Exabeam ووسع معرفتك في أمن المعلومات من خلال مجموعتنا من الأوراق البيضاء، البودكاست، الندوات، والمزيد.
-
 مدونة
Access Isn’t Trust: A Behavioral Risk Framework for People, Service Accounts, and AI Agents